Article
Audit GitLab CI/CD Drift with PowerShell
A practical PowerShell workflow for inventorying GitLab projects, collecting only CI-relevant files and identifying copied pipeline drift.
Topic
16 matching entries across Articles, TIL and Projects.
Long-form writing tagged PowerShell.
A practical PowerShell workflow for inventorying GitLab projects, collecting only CI-relevant files and identifying copied pipeline drift.
How I turned successful sandbox pipelines into narrow, reviewable GitLab merge requests without allowing automation to rewrite source repositories blindly.
How one broken release job became a repeatable audit, sandbox, verification and backport workflow for a mixed GitLab repository estate.
A practical standard for PowerShell that makes production automation predictable, testable, supportable and safe to change.
How to design backup automation that converges configuration safely, proves each run, controls retention and keeps restore testing separate from job success.
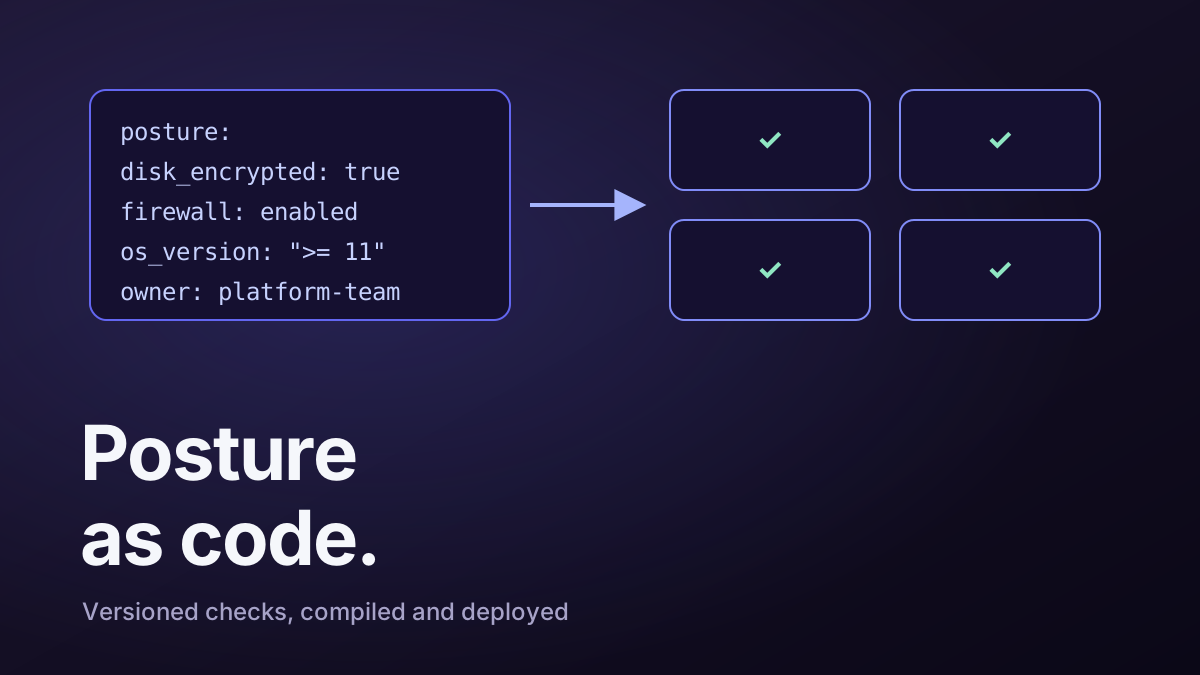
How to model, validate and deploy Cloudflare device posture checks as reusable configuration without coupling policy intent to environment-specific object IDs.
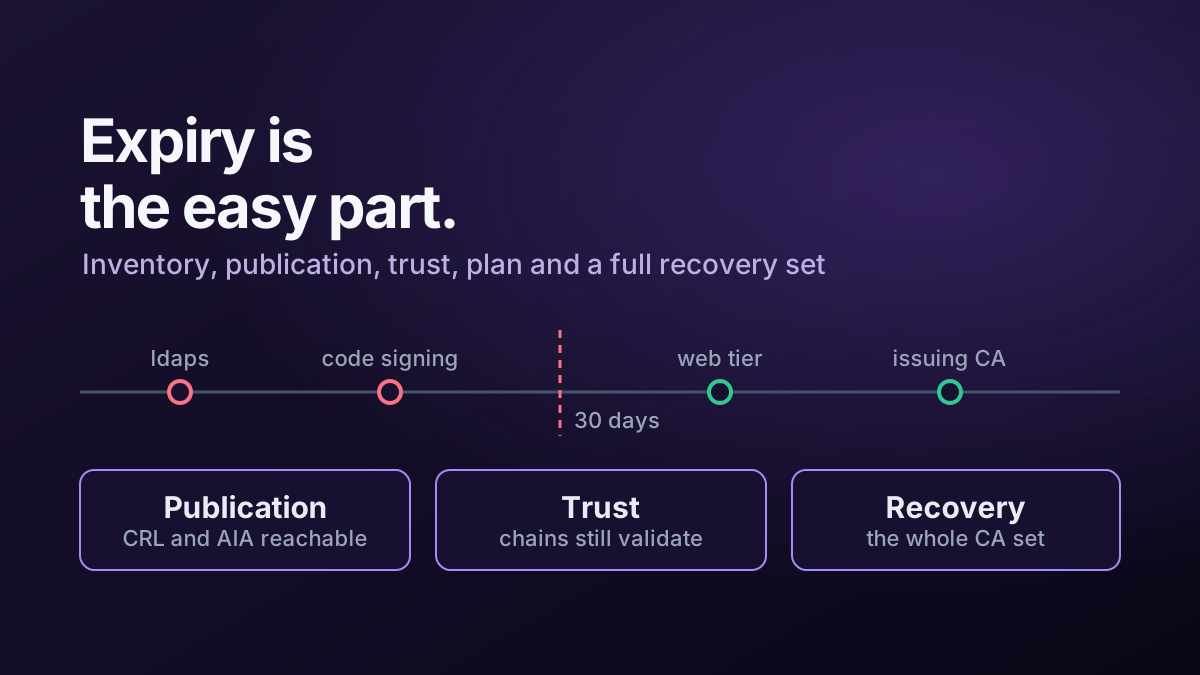
A safe pattern for automating PKI inventory, expiry monitoring, CA health checks, maintenance evidence and certificate lifecycle tasks without hiding risk.
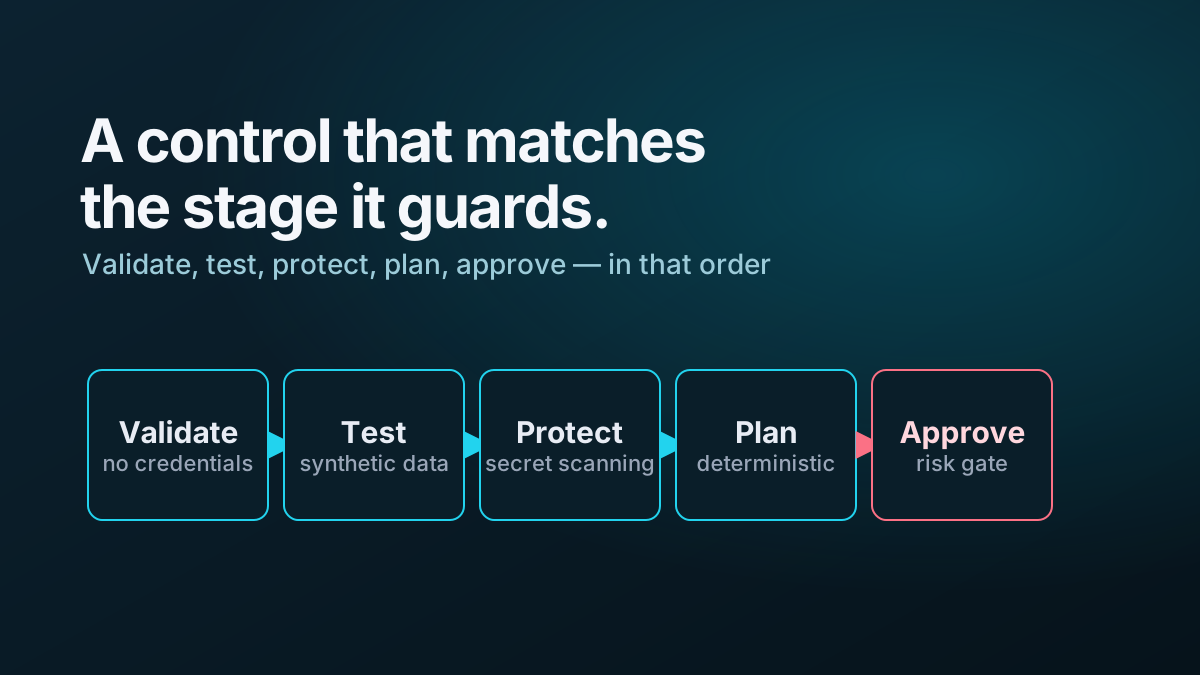
A practical DevSecOps pipeline for infrastructure changes: validate early, protect credentials, inspect plans, approve risk and retain deployment evidence.
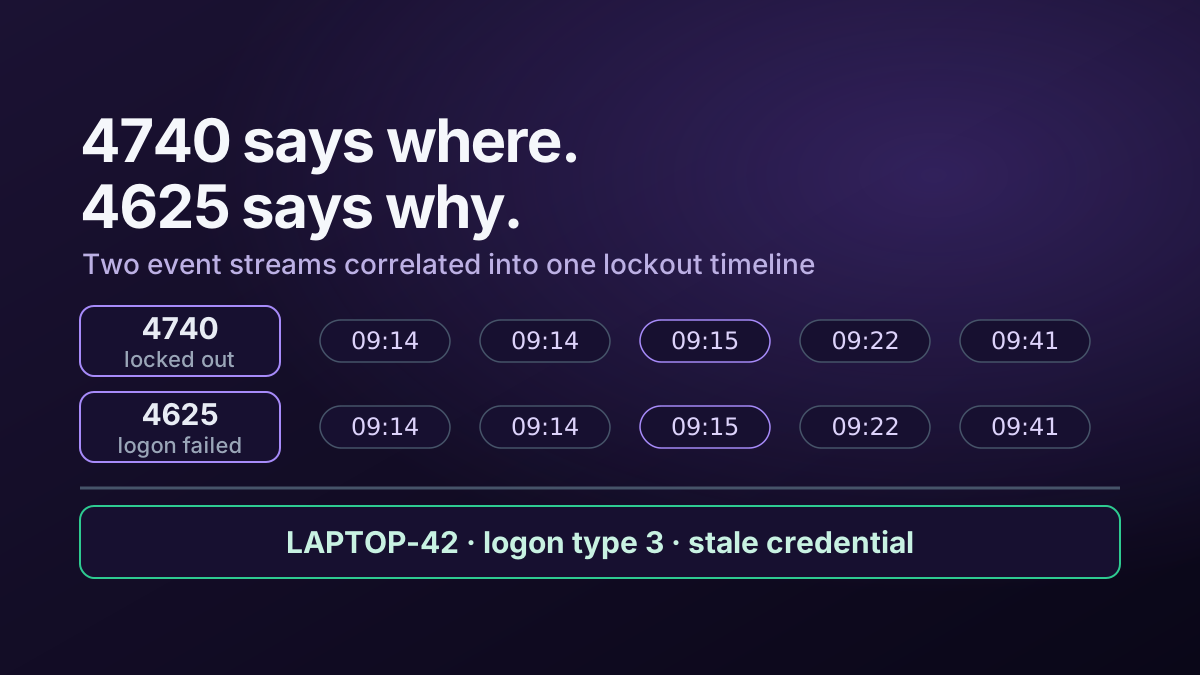
Use events 4740 and 4625 together to move from 'the account keeps locking' to a timeline that identifies the source device, logon type and stale credential.
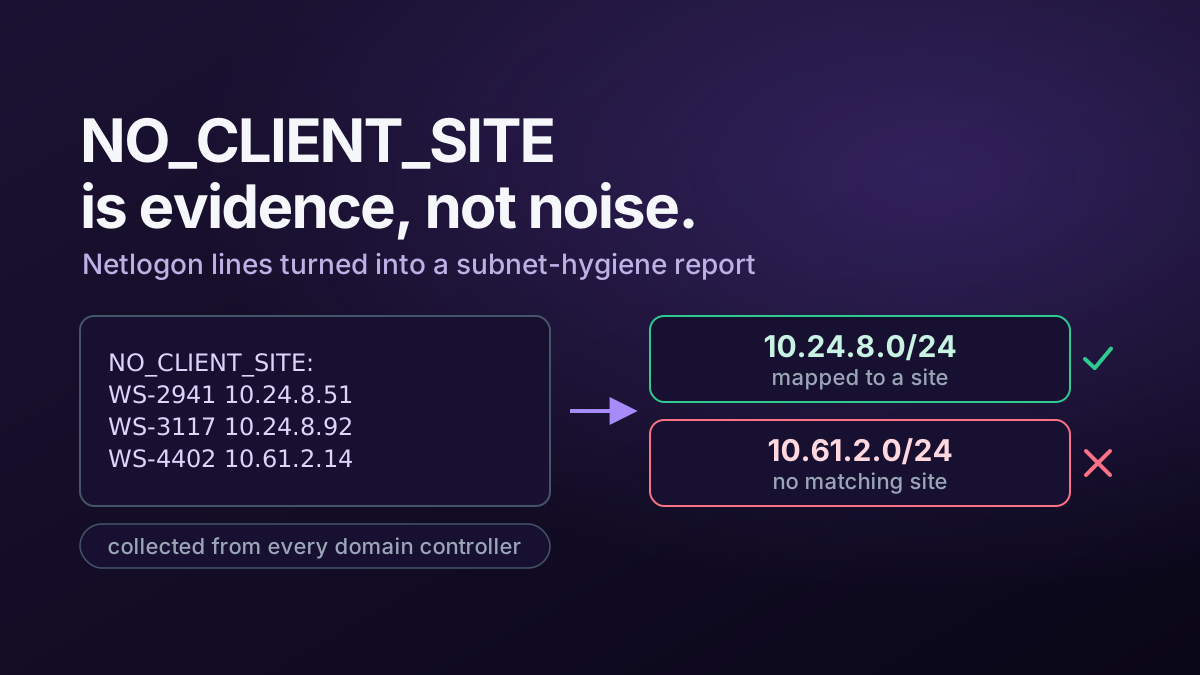
NO_CLIENT_SITE entries in Netlogon logs are useful evidence that client networks are not mapped cleanly to Active Directory sites. PowerShell can turn the logs into a subnet-hygiene report.
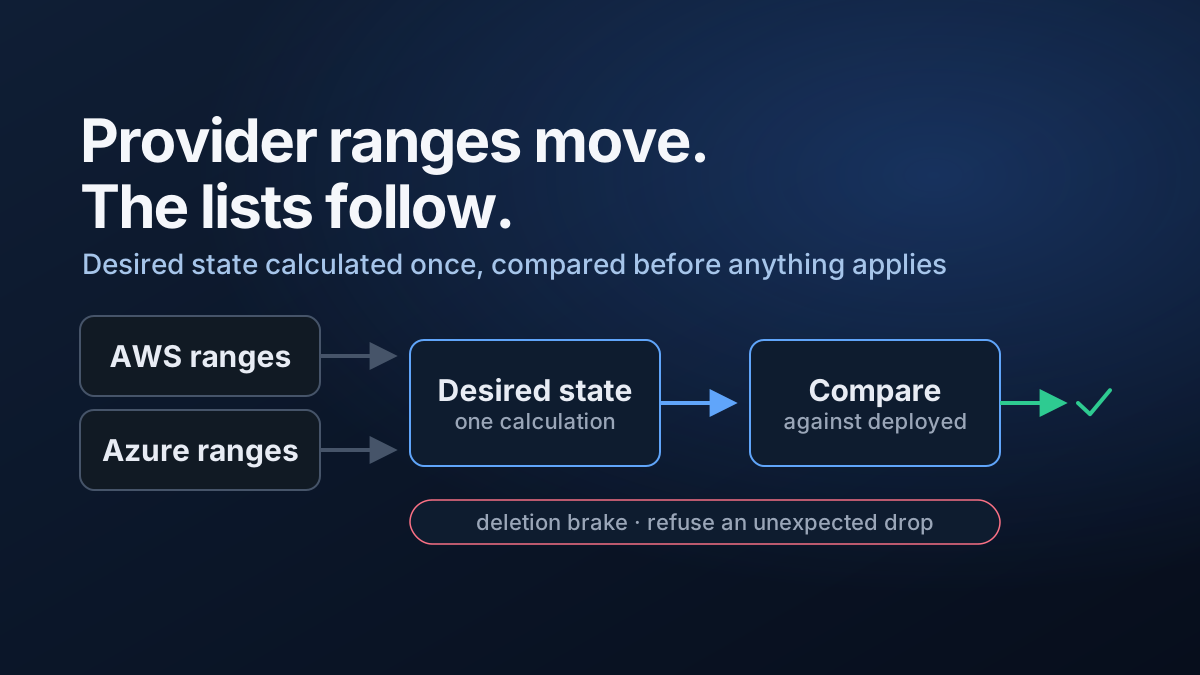
A practical pattern for consuming AWS/Azure network feeds, calculating desired state and safely synchronising Cloudflare Zero Trust lists with PowerShell.
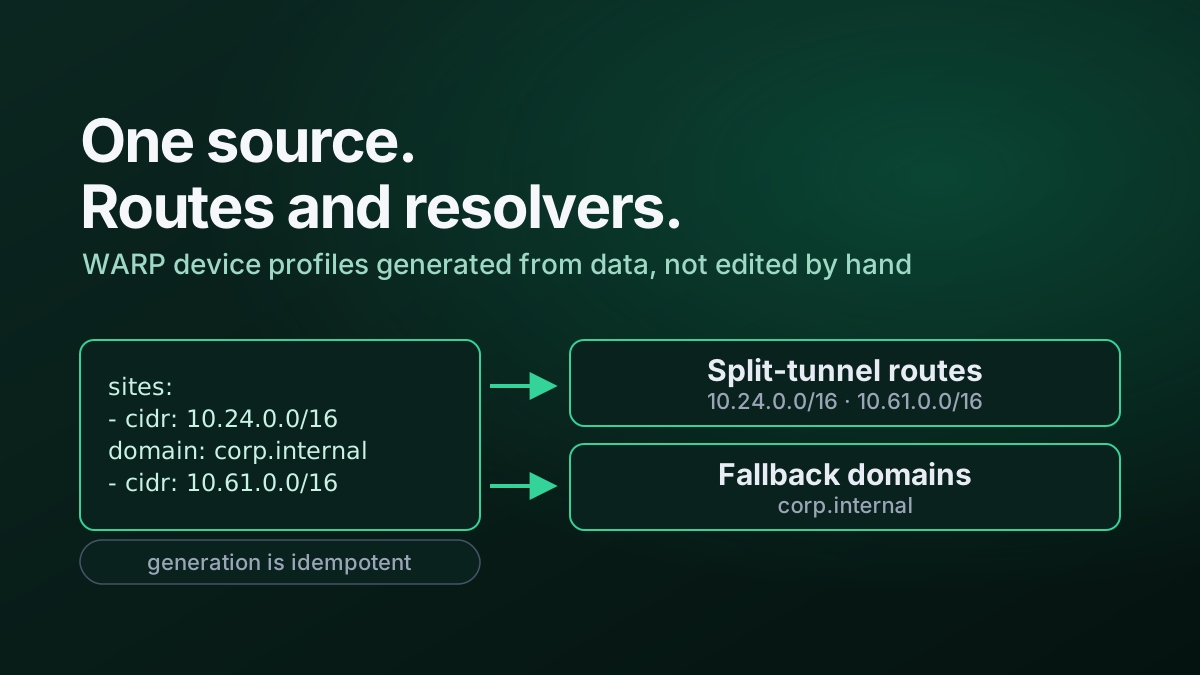
When private sites and DNS exceptions multiply, WARP device-profile configuration becomes data. Source control can become the input and PowerShell the generator.
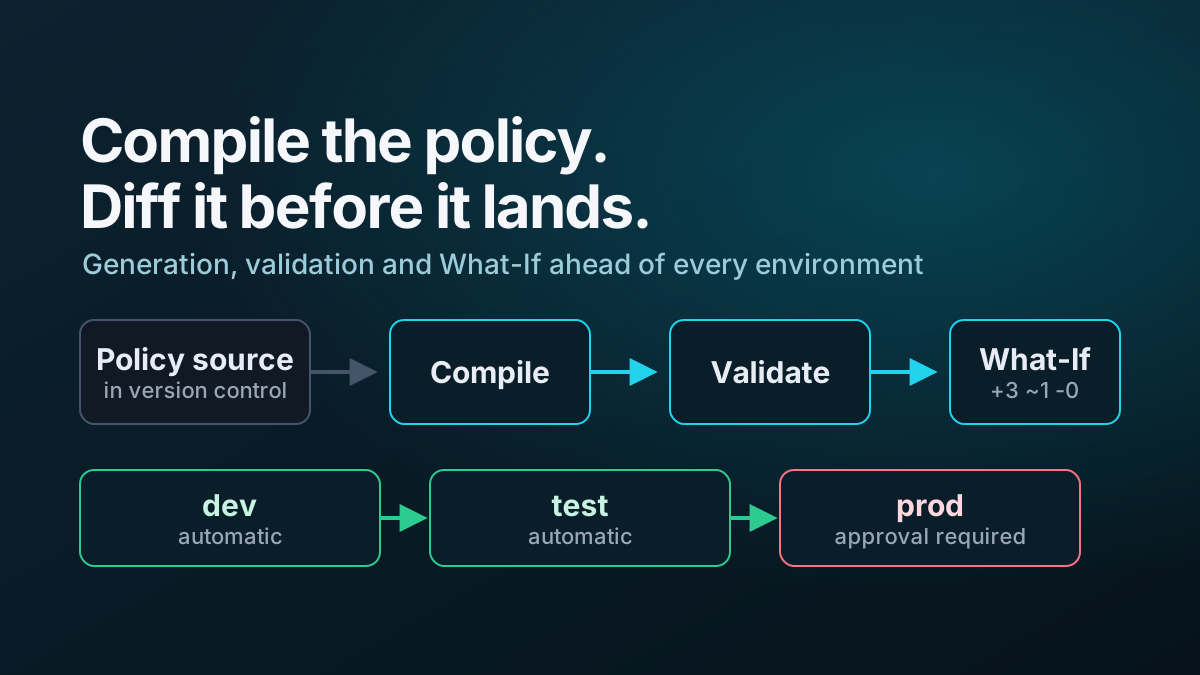
As Zero Trust policy grows, the engineering problem shifts from configuring a dashboard to safely compiling, validating and deploying policy across environments.
Short notes and fixes tagged PowerShell.
Why Active Directory exposes multiple logon attributes and why choosing the wrong one can give misleading results.
When a local script is blocked by execution policy, Process scope can be useful for a temporary session without changing the machine-wide setting.
Use a HEAD request to see the HTTP status and Location header without downloading the complete page.