Article
A Multi-Cloud Zero Trust Lab, Built in Terraform
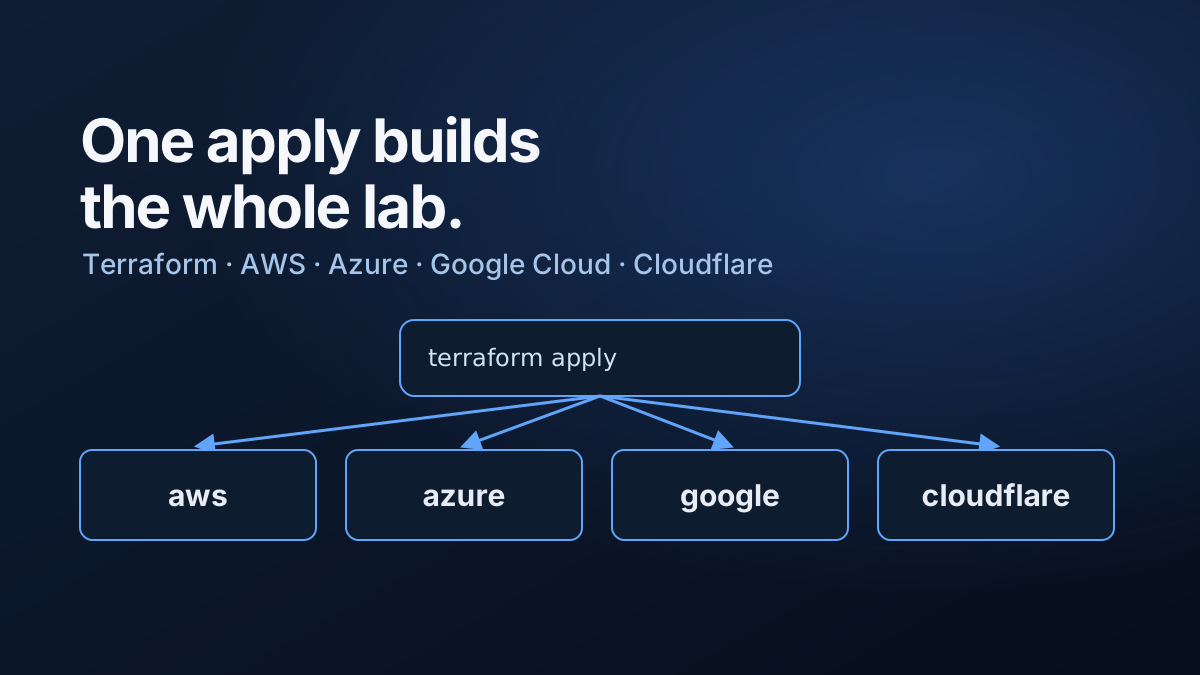
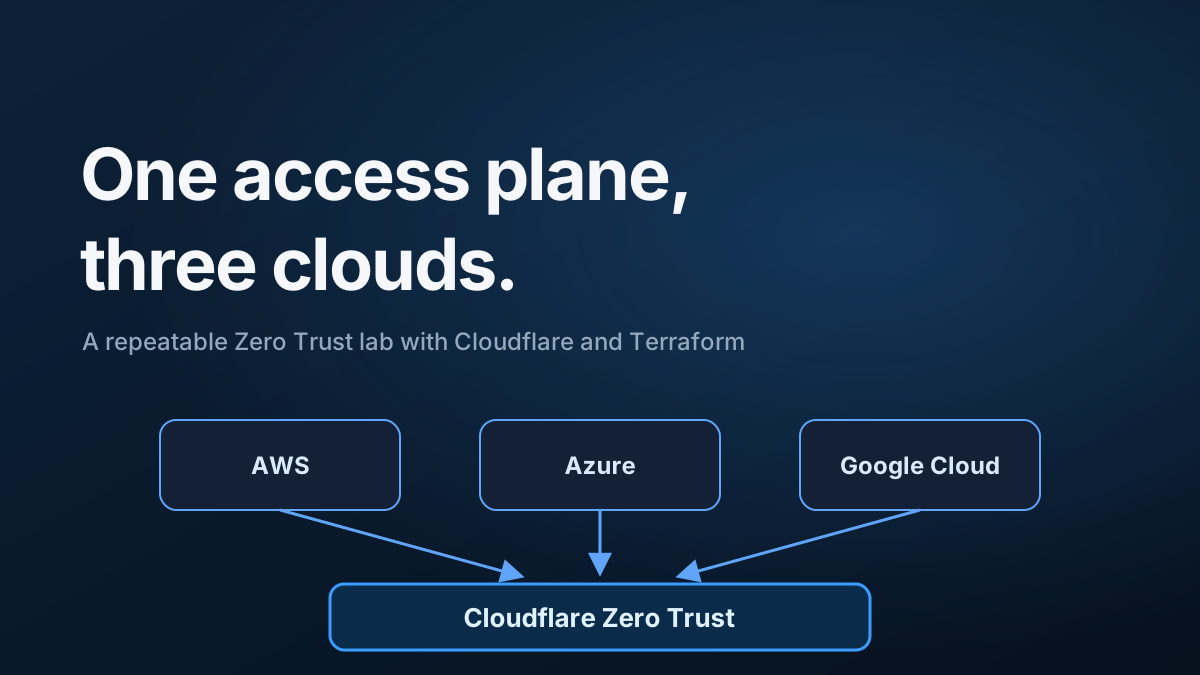
How I built a repeatable AWS, Azure and Google Cloud lab to explore Cloudflare Access, Gateway, WARP routing, device posture and external evaluation as one integrated Zero Trust system.
Topic
6 matching entries across Articles, TIL and Projects.
Long-form writing tagged Device Posture.
How I built a repeatable AWS, Azure and Google Cloud lab to explore Cloudflare Access, Gateway, WARP routing, device posture and external evaluation as one integrated Zero Trust system.
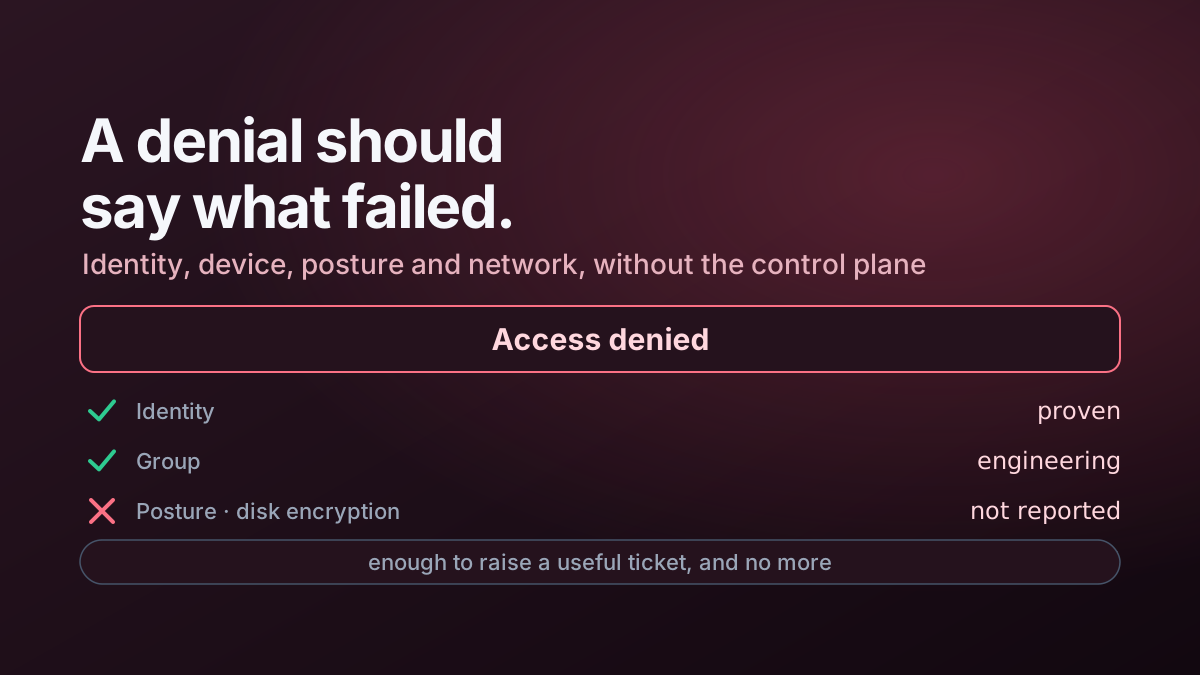
A custom Cloudflare Access denial page can turn a generic block into useful identity, device, posture and network diagnostics without exposing sensitive control-plane details.
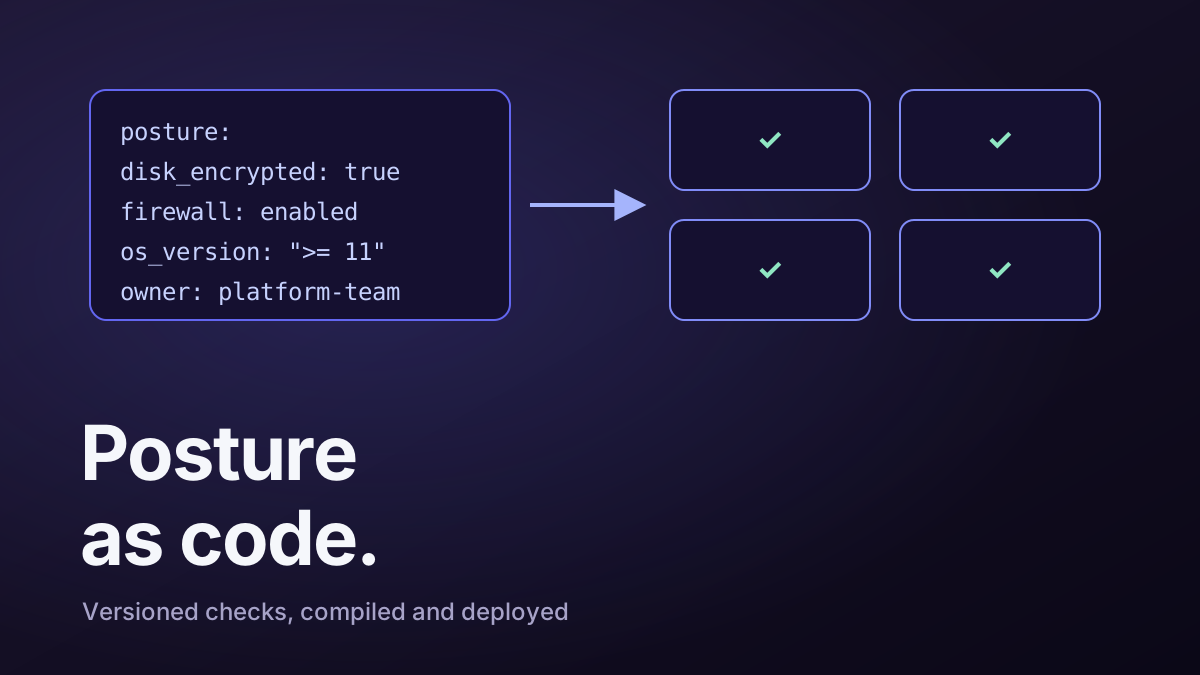
How to model, validate and deploy Cloudflare device posture checks as reusable configuration without coupling policy intent to environment-specific object IDs.
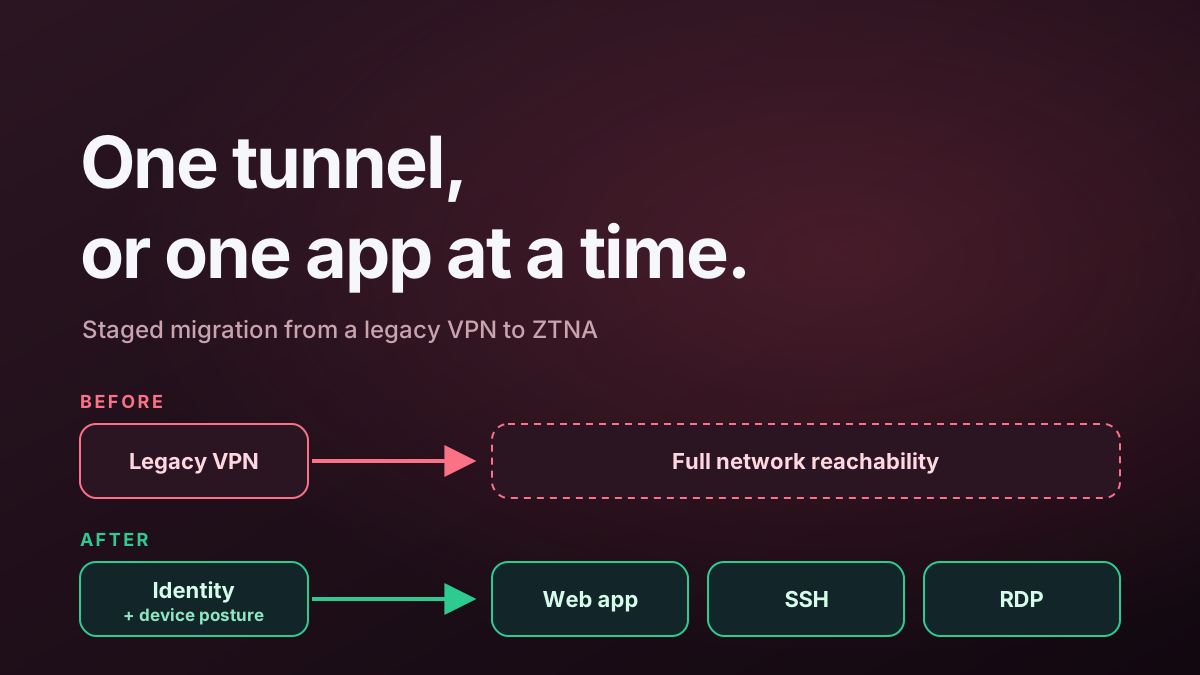
Practical lessons from an enterprise ZTNA deployment: foundations, staged migration, policy automation, legacy applications, change management, and measurement.
Projects and implementation patterns tagged Device Posture.
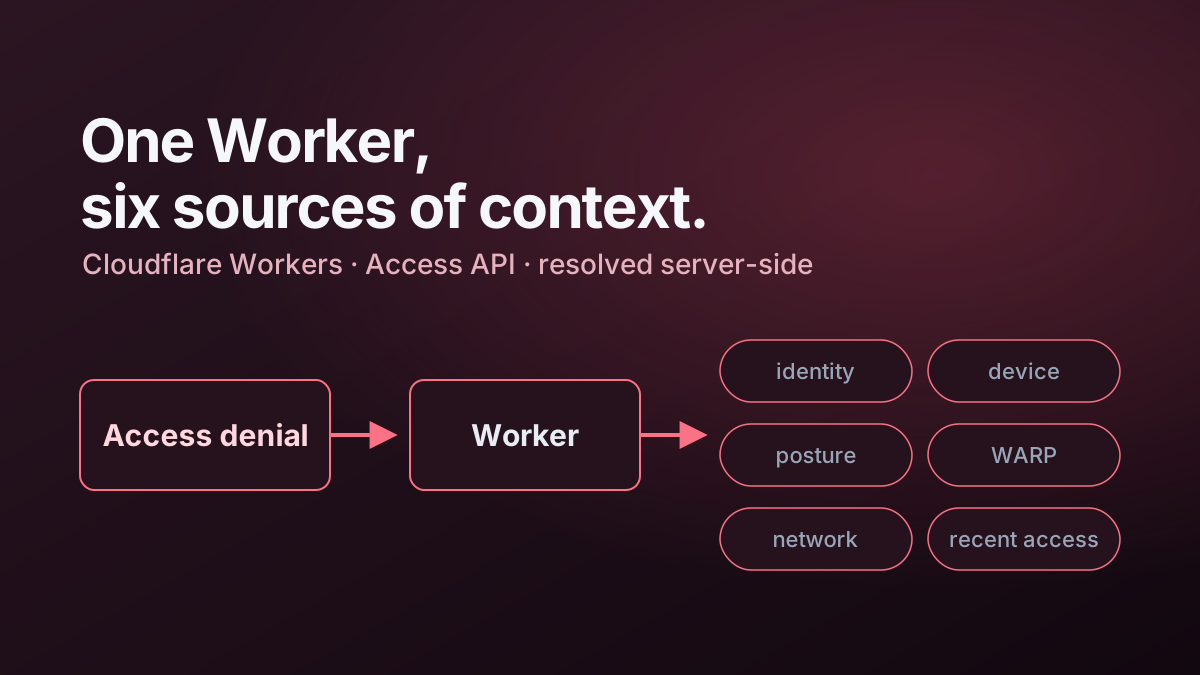
A Cloudflare Worker that turns an Access denial into a support-friendly diagnostic page with identity, device, posture, WARP, network and recent-access context.
A Terraform-managed Zero Trust engineering lab spanning AWS, Azure and Google Cloud with Cloudflare Access, Gateway, WARP routing, device posture and optional Worker integrations.