Article
A Multi-Cloud Zero Trust Lab, Built in Terraform
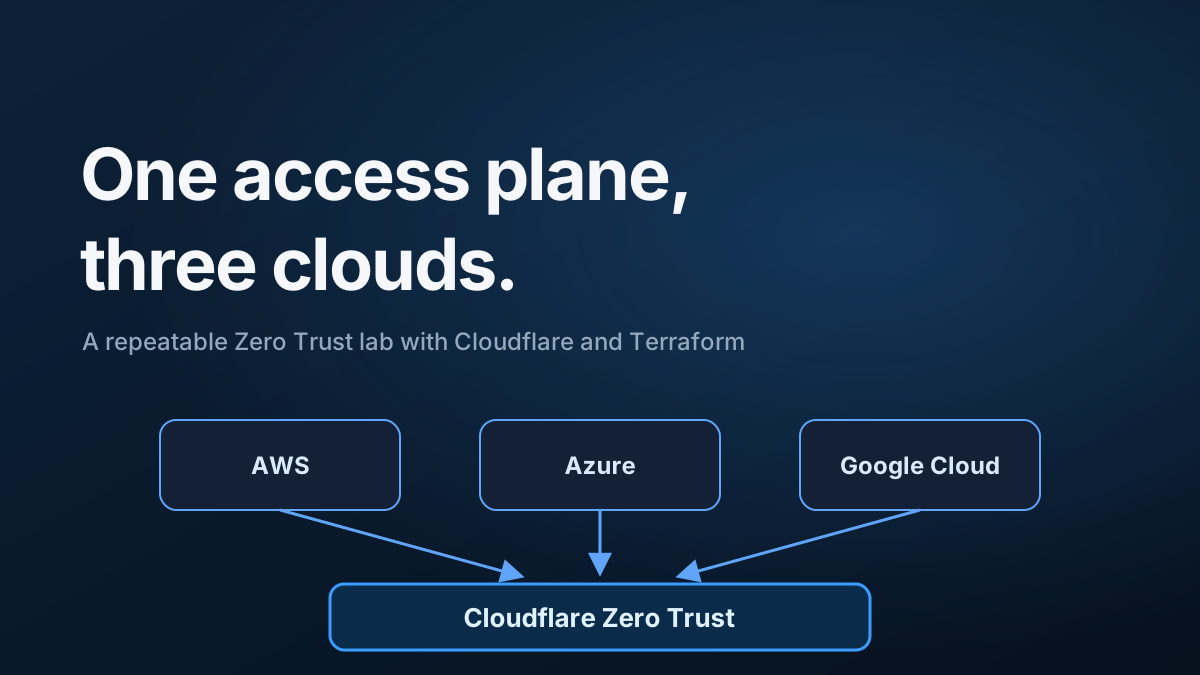
How I built a repeatable AWS, Azure and Google Cloud lab to explore Cloudflare Access, Gateway, WARP routing, device posture and external evaluation as one integrated Zero Trust system.
Topic
7 matching entries across Articles, TIL and Projects.
Long-form writing tagged Access.
How I built a repeatable AWS, Azure and Google Cloud lab to explore Cloudflare Access, Gateway, WARP routing, device posture and external evaluation as one integrated Zero Trust system.
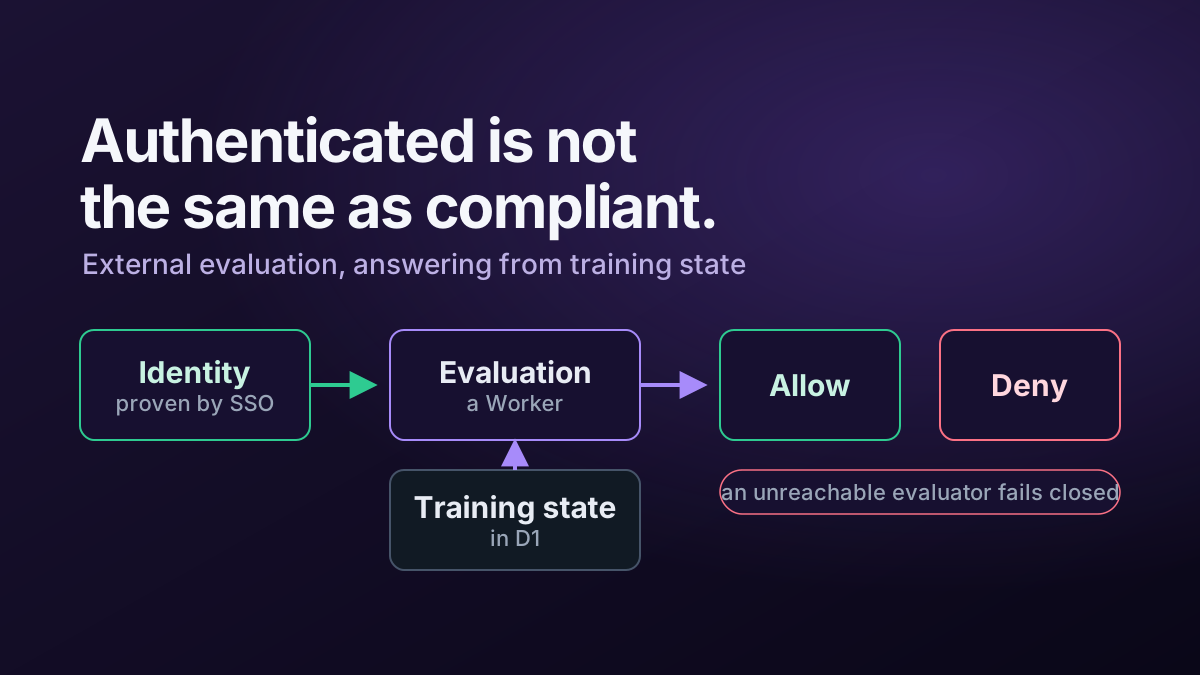
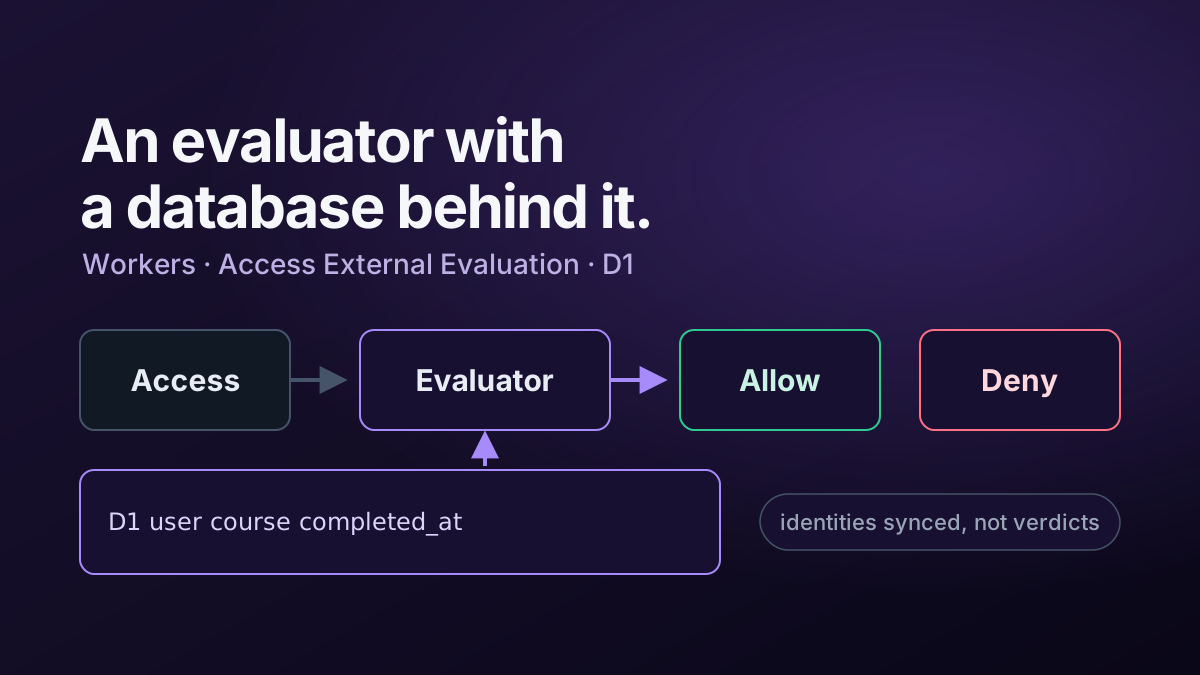
Authentication proves identity, but it does not prove a user has met a business requirement. I used Cloudflare Access External Evaluation, Workers and D1 to add training compliance to the access decision.
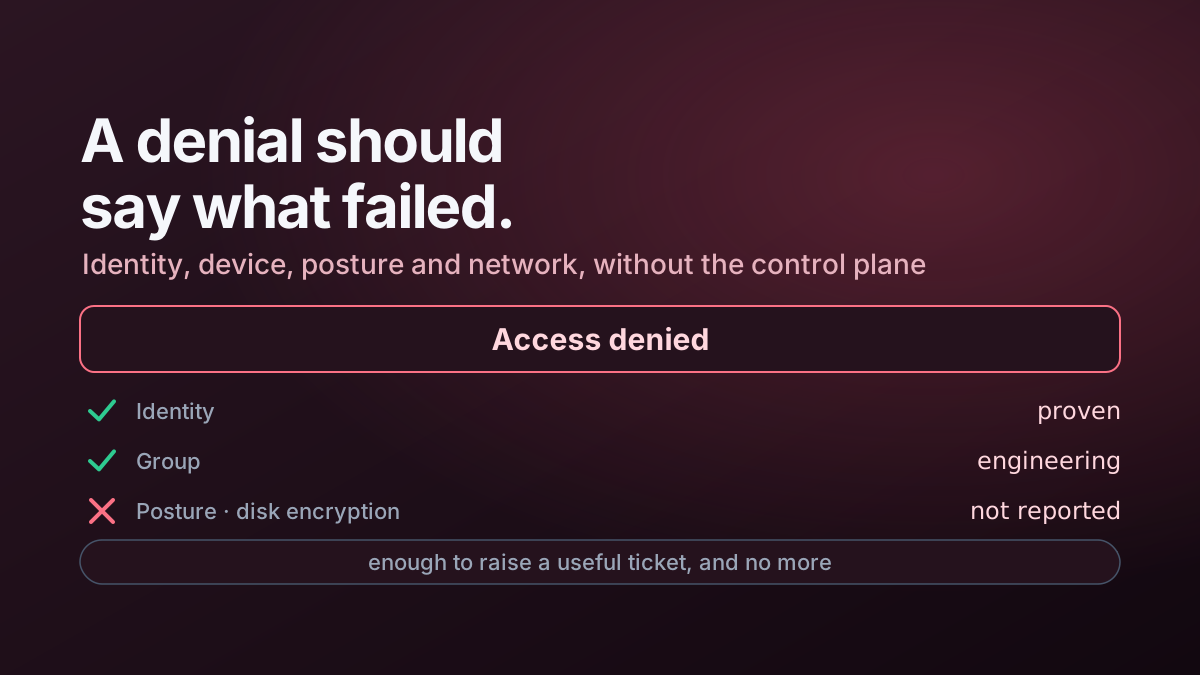
A custom Cloudflare Access denial page can turn a generic block into useful identity, device, posture and network diagnostics without exposing sensitive control-plane details.
Short notes and fixes tagged Access.
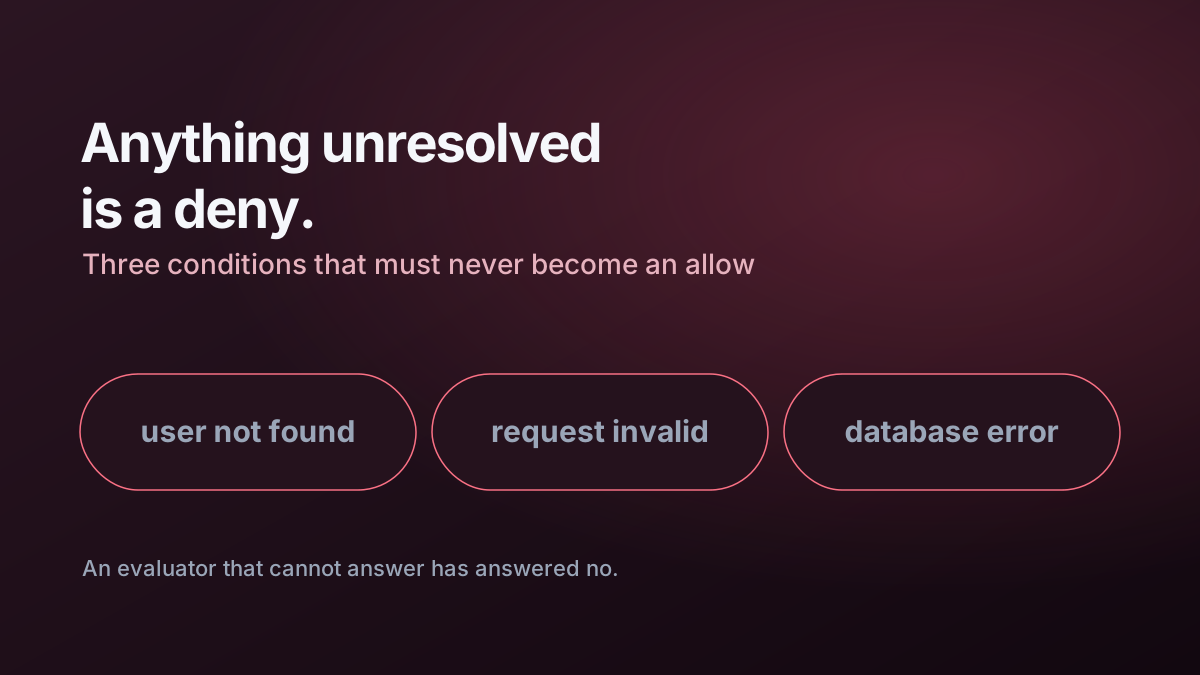
For a training-compliance Access evaluator, I treat missing users, invalid requests and database errors as deny conditions instead of accidental allows.
Projects and implementation patterns tagged Access.
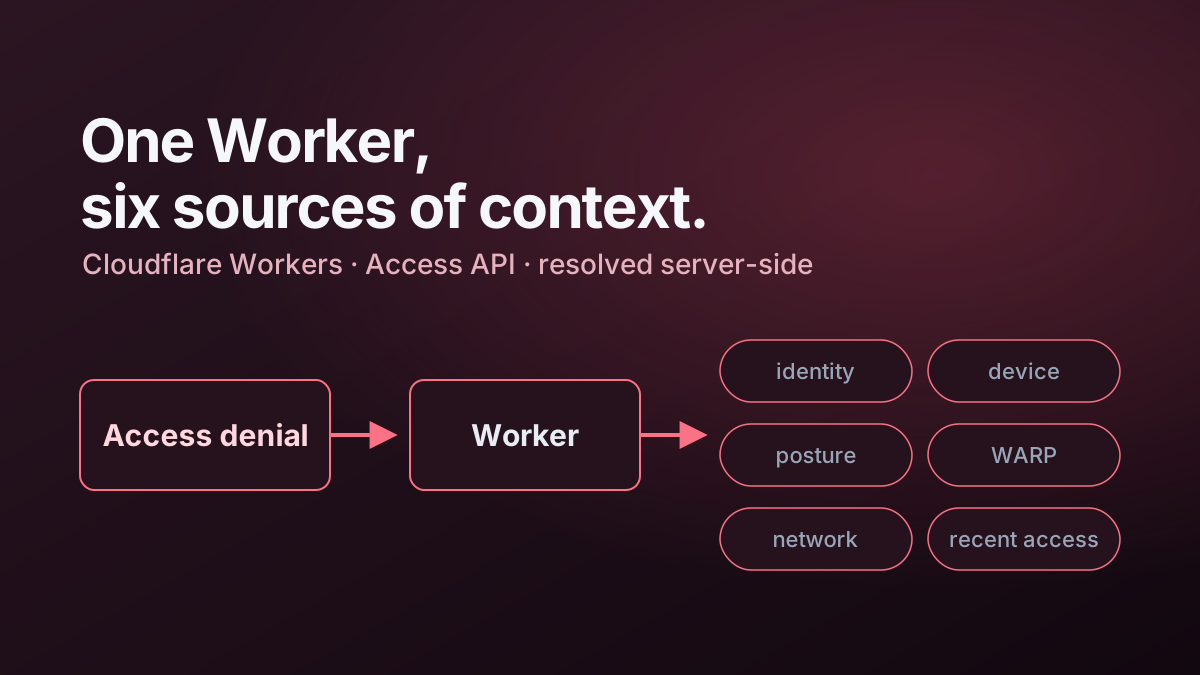
A Cloudflare Worker that turns an Access denial into a support-friendly diagnostic page with identity, device, posture, WARP, network and recent-access context.
A Terraform-managed Zero Trust engineering lab spanning AWS, Azure and Google Cloud with Cloudflare Access, Gateway, WARP routing, device posture and optional Worker integrations.
An Access External Evaluation Worker that uses D1-backed training state to require mandatory training completion before protected applications can be opened.