Article
A Multi-Cloud Zero Trust Lab, Built in Terraform
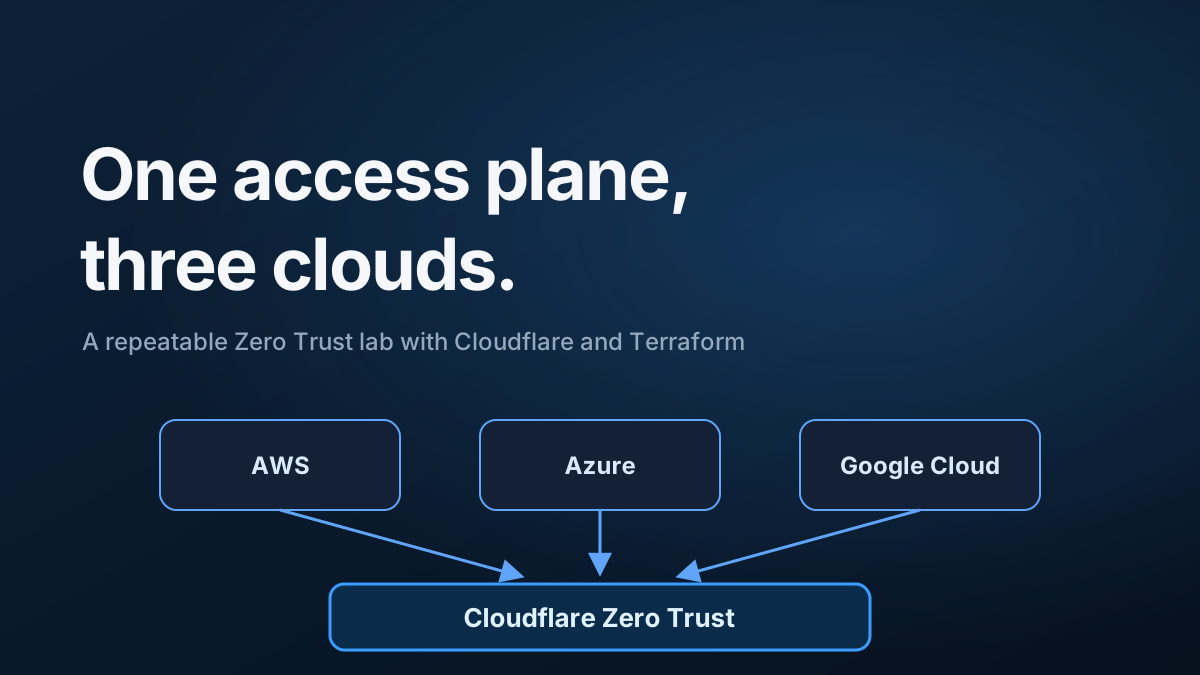
How I built a repeatable AWS, Azure and Google Cloud lab to explore Cloudflare Access, Gateway, WARP routing, device posture and external evaluation as one integrated Zero Trust system.
Topic
4 matching entries across Articles, TIL and Projects.
Long-form writing tagged AWS.
How I built a repeatable AWS, Azure and Google Cloud lab to explore Cloudflare Access, Gateway, WARP routing, device posture and external evaluation as one integrated Zero Trust system.
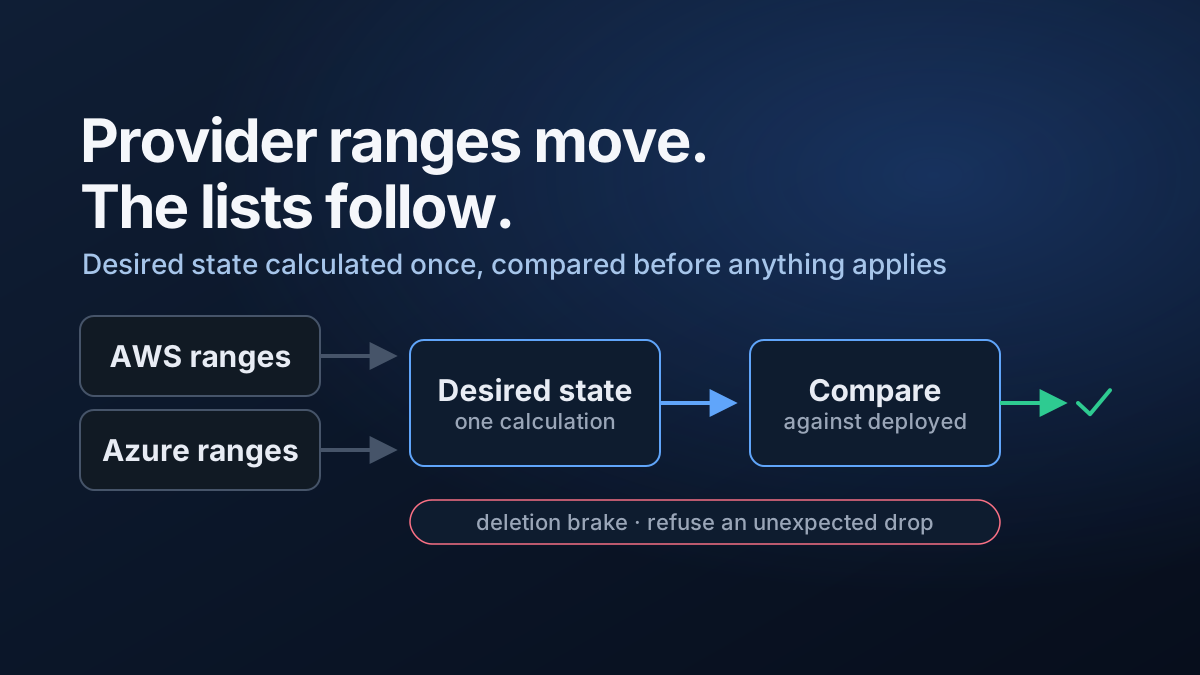
A practical pattern for consuming AWS/Azure network feeds, calculating desired state and safely synchronising Cloudflare Zero Trust lists with PowerShell.
Short notes and fixes tagged AWS.
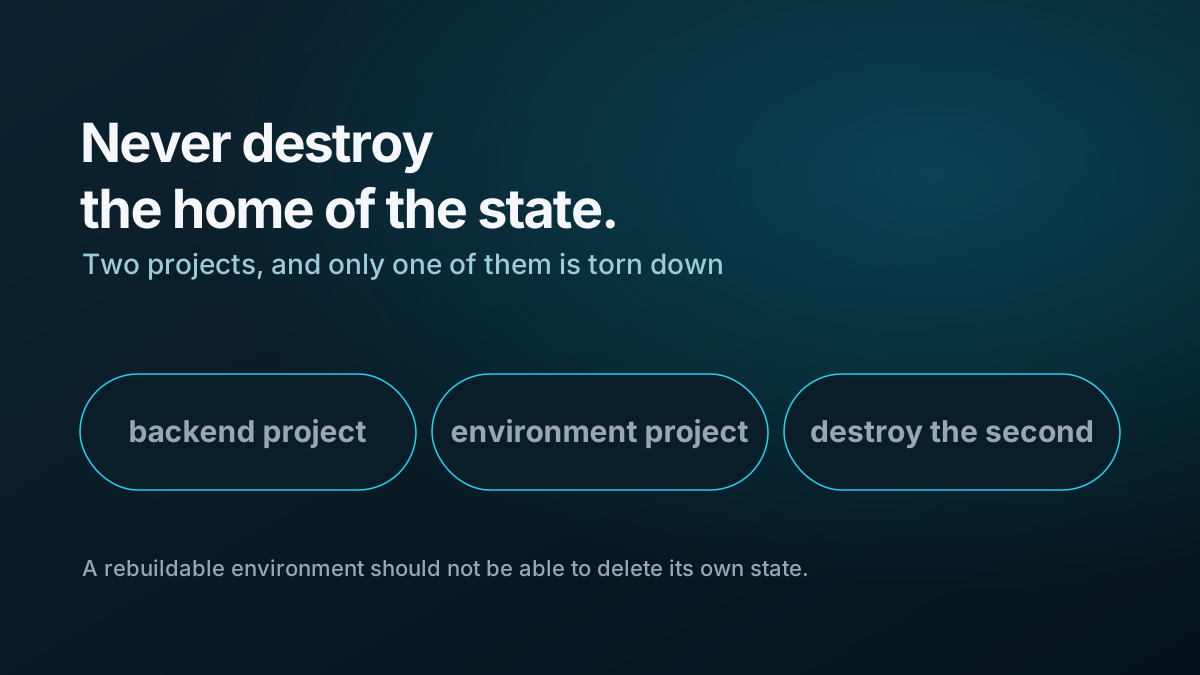
A rebuildable demo environment should not destroy the backend that stores its state, so I manage the S3/DynamoDB backend as a separate Terraform project.
Projects and implementation patterns tagged AWS.
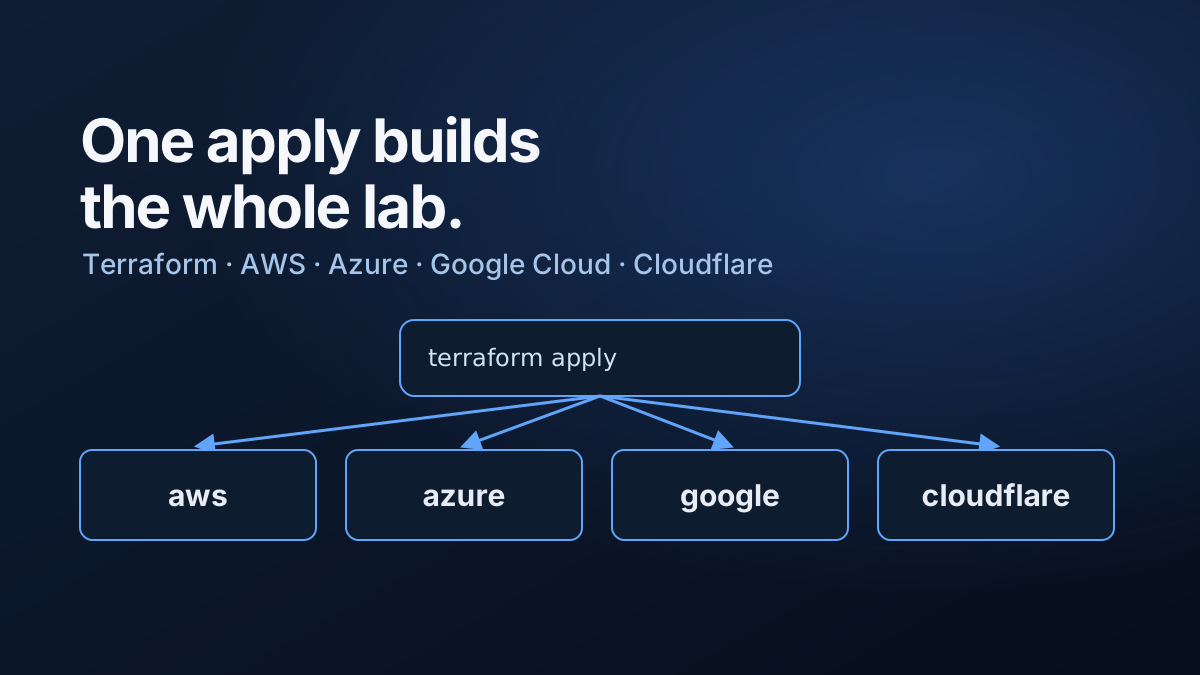
A Terraform-managed Zero Trust engineering lab spanning AWS, Azure and Google Cloud with Cloudflare Access, Gateway, WARP routing, device posture and optional Worker integrations.