Article
Cloudflare DNS Ad Blocking with Terraform
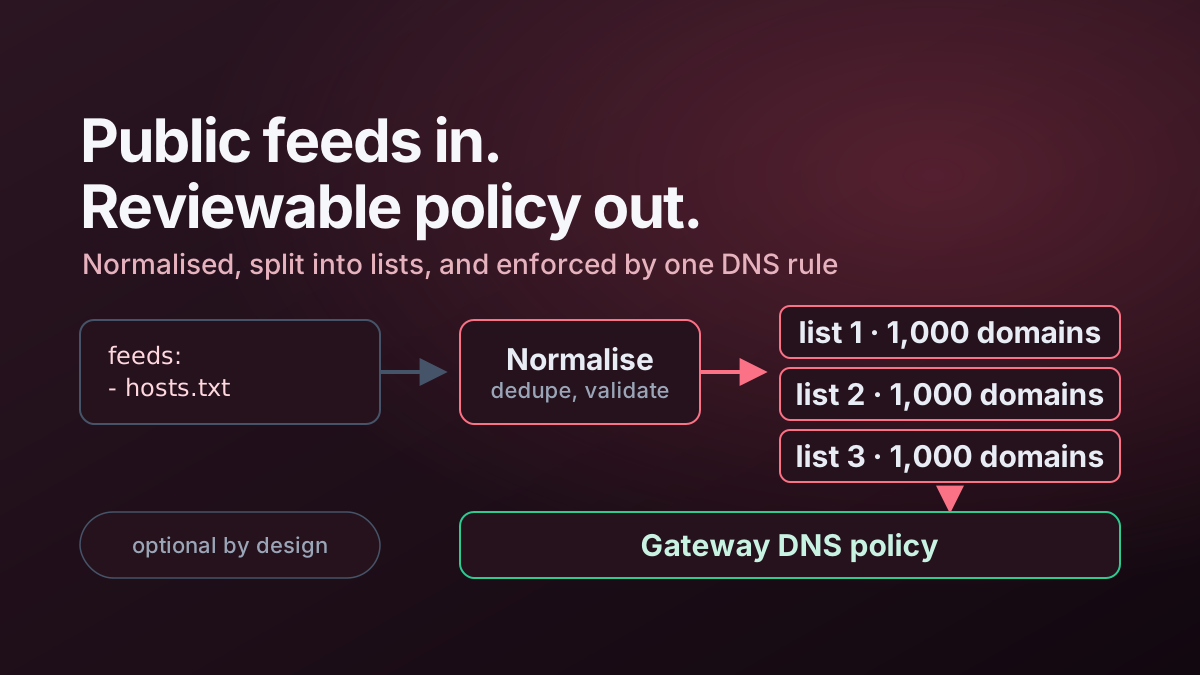
I used Terraform to fetch public domain feeds, turn them into Cloudflare Zero Trust lists and enforce them with a Gateway DNS policy that remains reviewable as code.
Topic
4 matching entries across Articles, TIL and Projects.
Long-form writing tagged Infrastructure as Code.
I used Terraform to fetch public domain feeds, turn them into Cloudflare Zero Trust lists and enforce them with a Gateway DNS policy that remains reviewable as code.
Short notes and fixes tagged Infrastructure as Code.
A rebuildable demo environment should not destroy the backend that stores its state, so I manage the S3/DynamoDB backend as a separate Terraform project.
An HTTP data source can retrieve an external domain feed, but the useful pattern is to validate and normalize it before Terraform materializes enforcement objects.
Projects and implementation patterns tagged Infrastructure as Code.
A Terraform project that consumes remote domain feeds, normalizes them into Cloudflare Zero Trust lists and builds a Gateway DNS blocking policy from the generated data.