Article
Building a Better Cloudflare Gateway Block Page
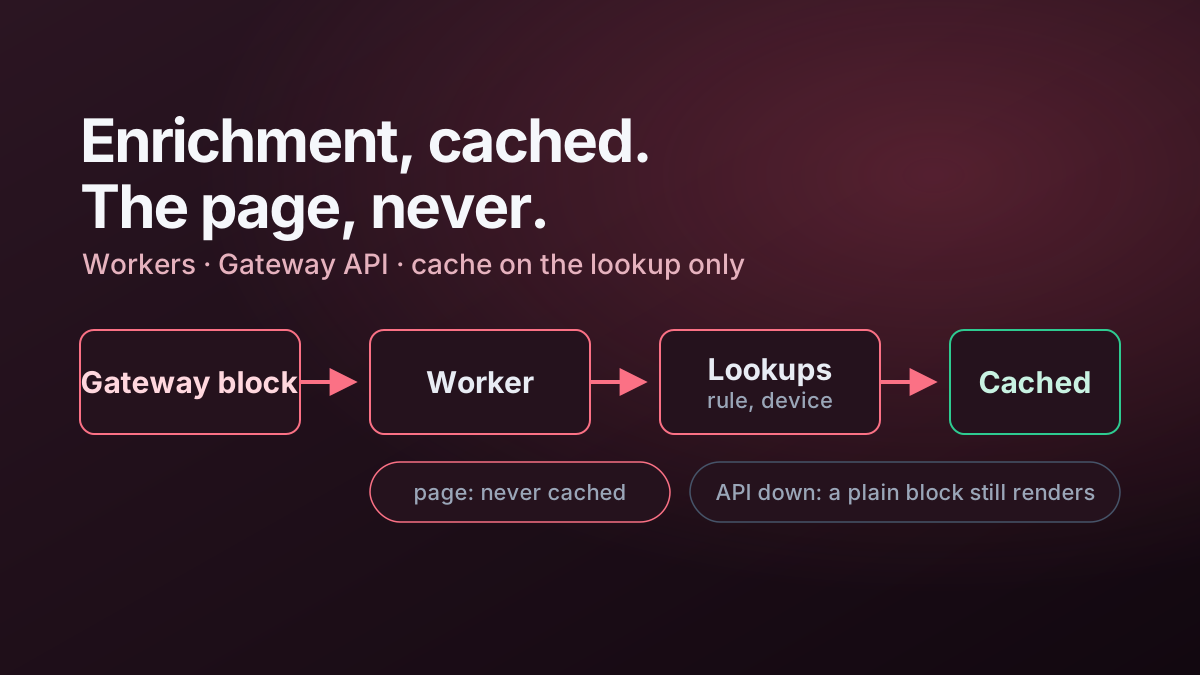
How I used a Cloudflare Worker to enrich Gateway blocks with policy, device, user, category and Cloudflare One Client context while keeping the page resilient and secure.
Topic
12 matching entries across Articles, TIL and Projects.
Long-form writing tagged Gateway.
How I used a Cloudflare Worker to enrich Gateway blocks with policy, device, user, category and Cloudflare One Client context while keeping the page resilient and secure.
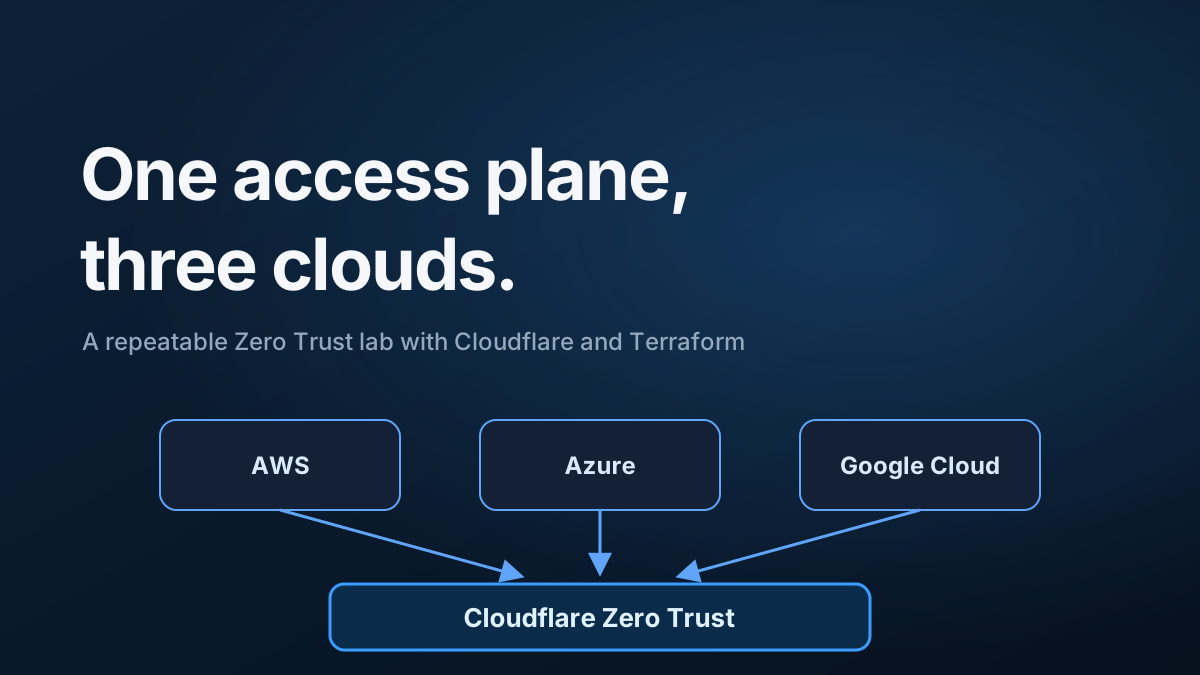
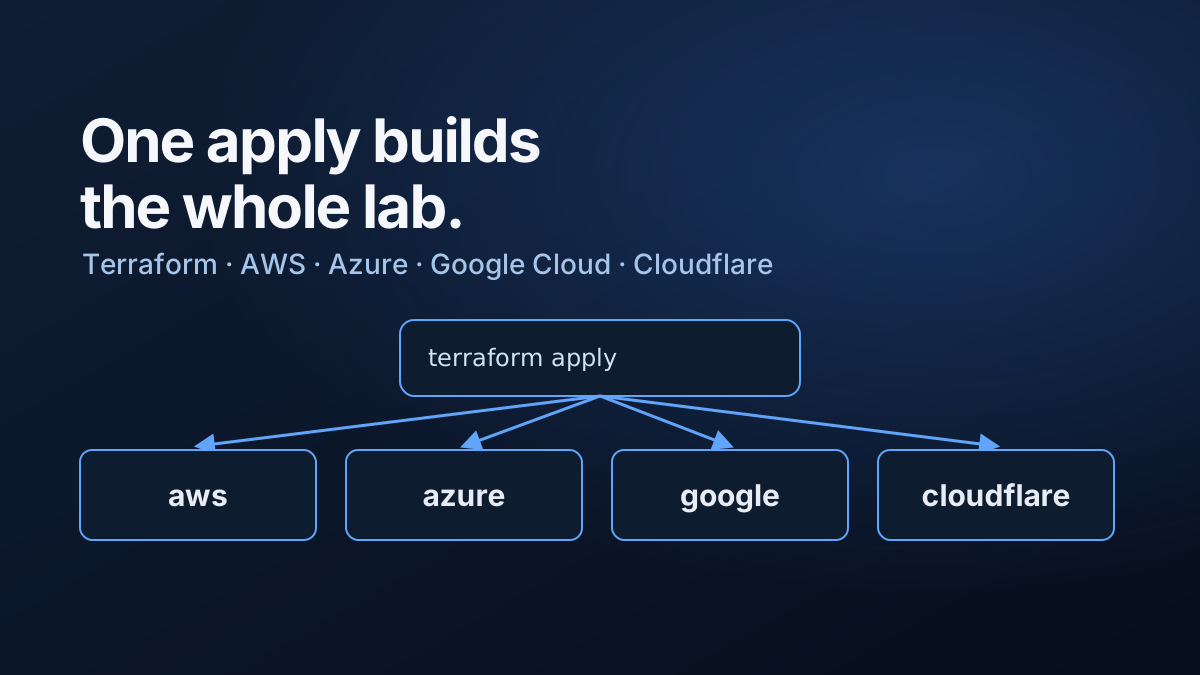
How I built a repeatable AWS, Azure and Google Cloud lab to explore Cloudflare Access, Gateway, WARP routing, device posture and external evaluation as one integrated Zero Trust system.
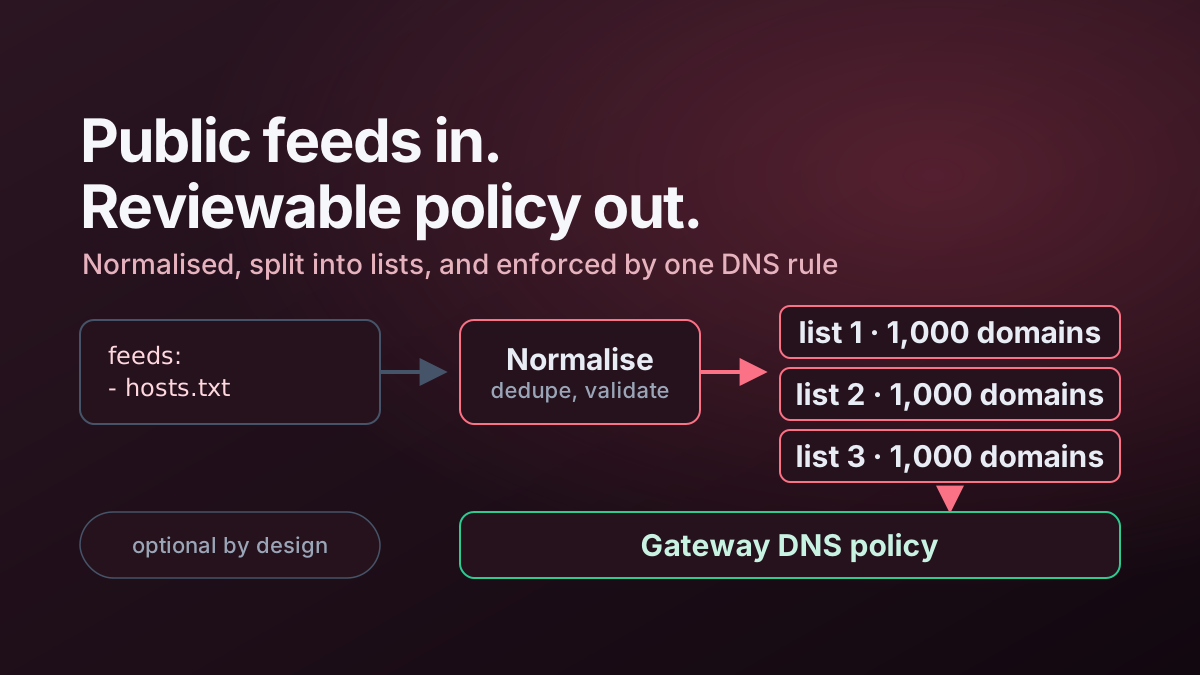
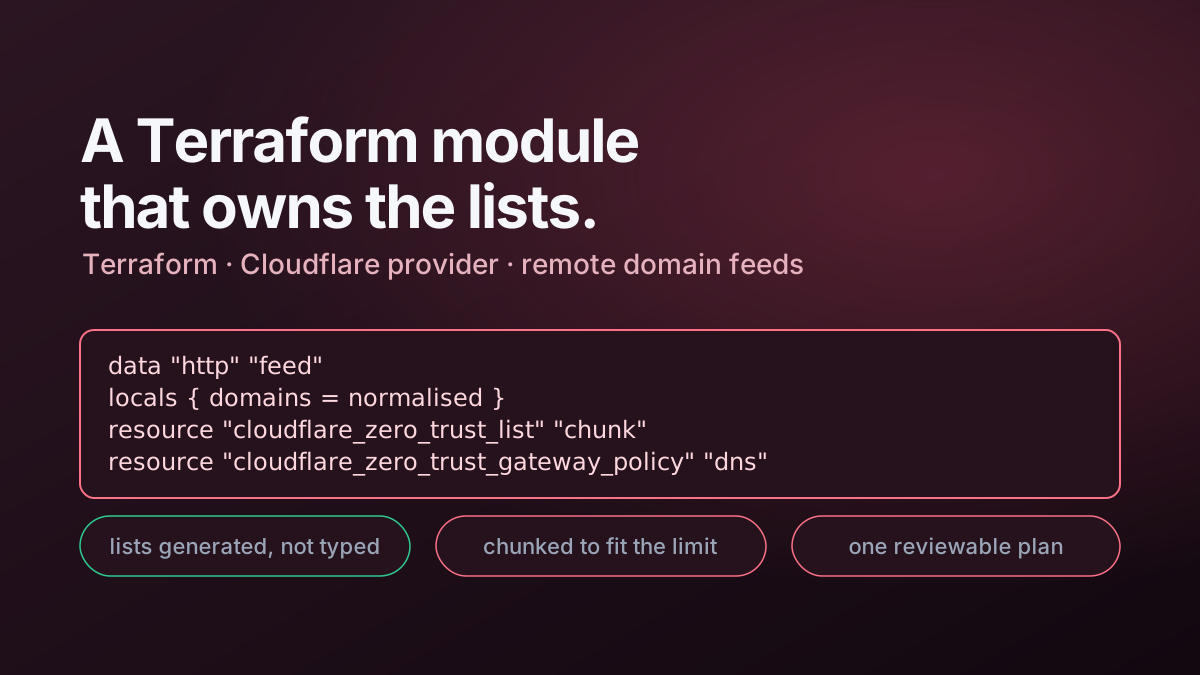
I used Terraform to fetch public domain feeds, turn them into Cloudflare Zero Trust lists and enforce them with a Gateway DNS policy that remains reviewable as code.
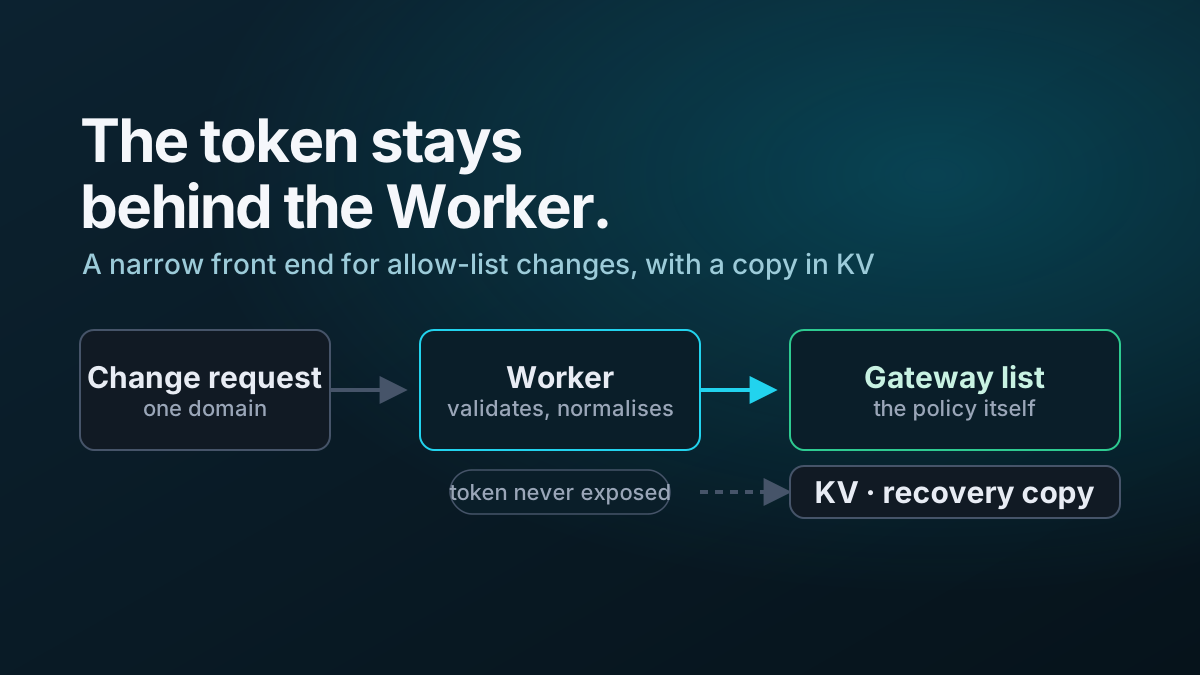
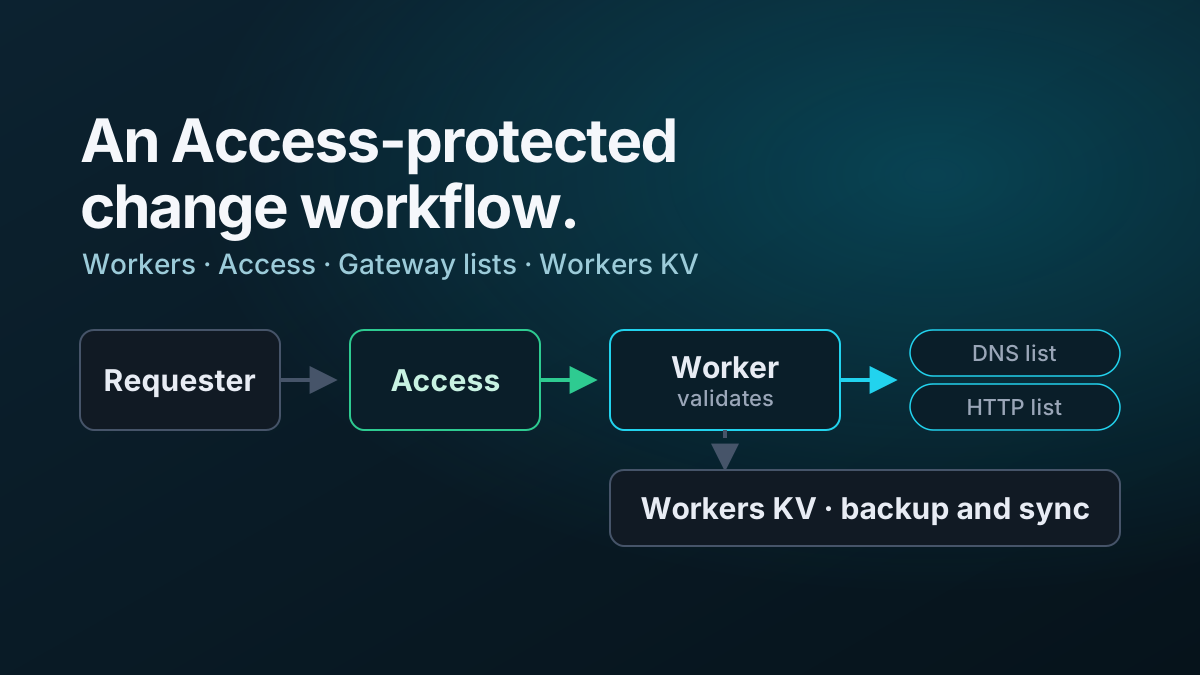
A small Cloudflare Worker can provide a controlled front end for Gateway allow-list changes while KV supplies recovery, synchronization and operational visibility.
Short notes and fixes tagged Gateway.
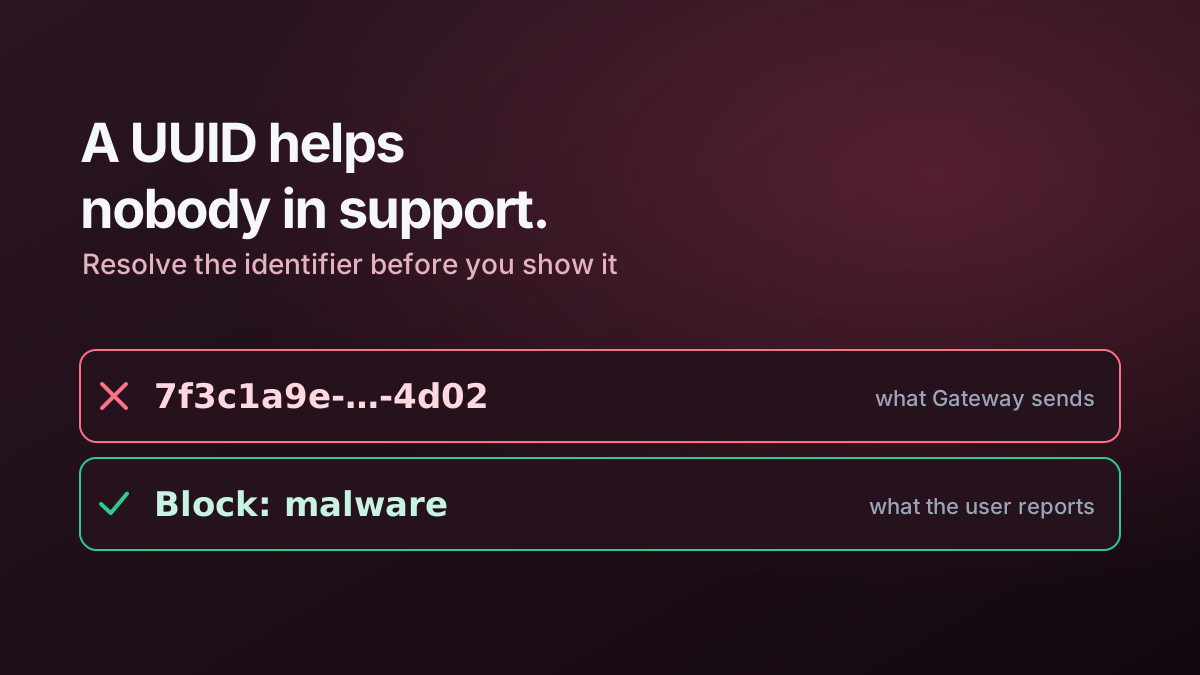
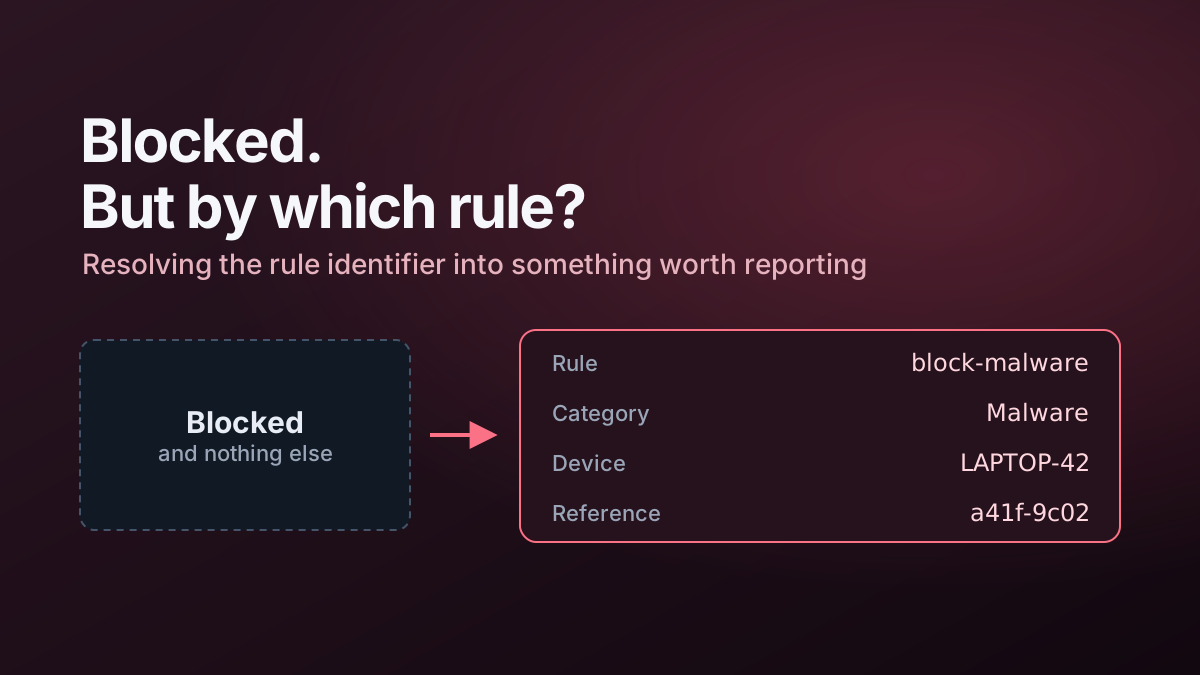
Cloudflare Gateway can provide a rule ID to a custom block page, but resolving that UUID to the rule name makes support diagnostics much more useful.
A CF-Ray header alone does not prove a request came from Gateway, so my Worker requires Gateway-specific query context before rendering diagnostic output.
An HTTP data source can retrieve an external domain feed, but the useful pattern is to validate and normalize it before Terraform materializes enforcement objects.
In my Gateway allow-list Worker, Cloudflare lists remain the enforcement state while Workers KV stores backup and synchronization metadata.
Projects and implementation patterns tagged Gateway.
A Cloudflare Worker that provides a narrow, Access-protected workflow for validated Gateway allow-list changes with DNS/HTTP targeting and Workers KV backup.
A Terraform project that consumes remote domain feeds, normalizes them into Cloudflare Zero Trust lists and builds a Gateway DNS blocking policy from the generated data.
A Cloudflare Worker that enriches Gateway blocks with rule names, request category, user, device, Cloudflare One Client addresses and support correlation data.
A Terraform-managed Zero Trust engineering lab spanning AWS, Azure and Google Cloud with Cloudflare Access, Gateway, WARP routing, device posture and optional Worker integrations.