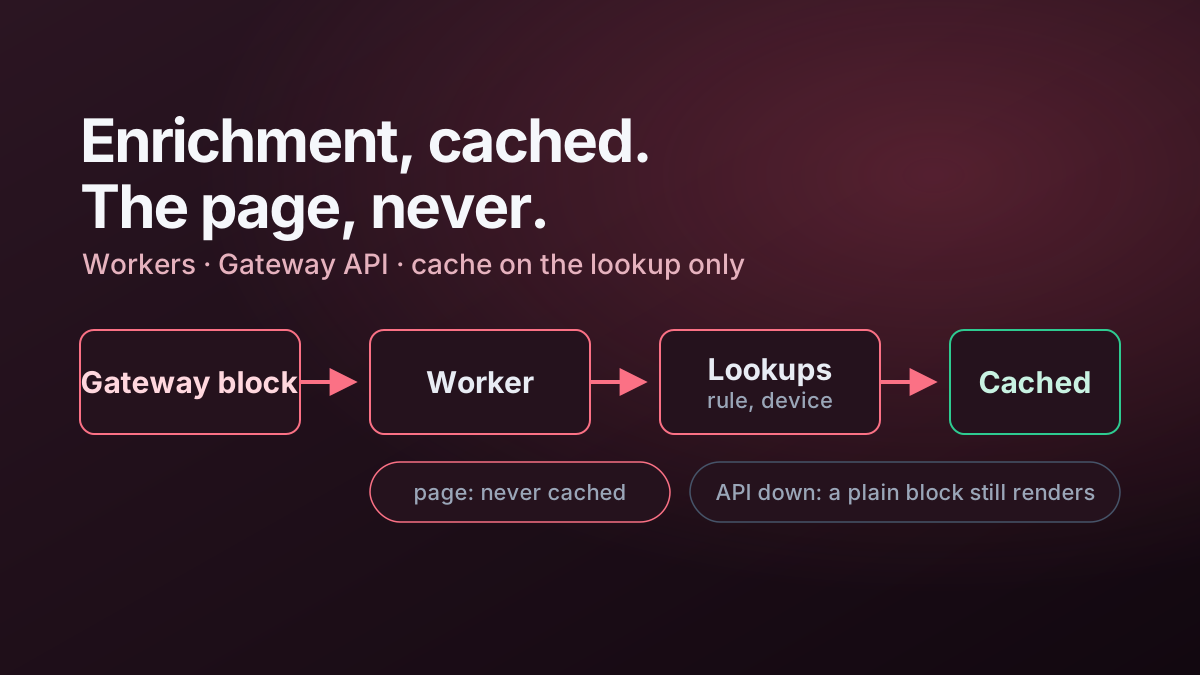
A Worker behind Cloudflare receives ordinary Cloudflare headers even when somebody visits its URL directly.
That means a value such as CF-Ray is not sufficient evidence that the request is a real Gateway block-page redirect.
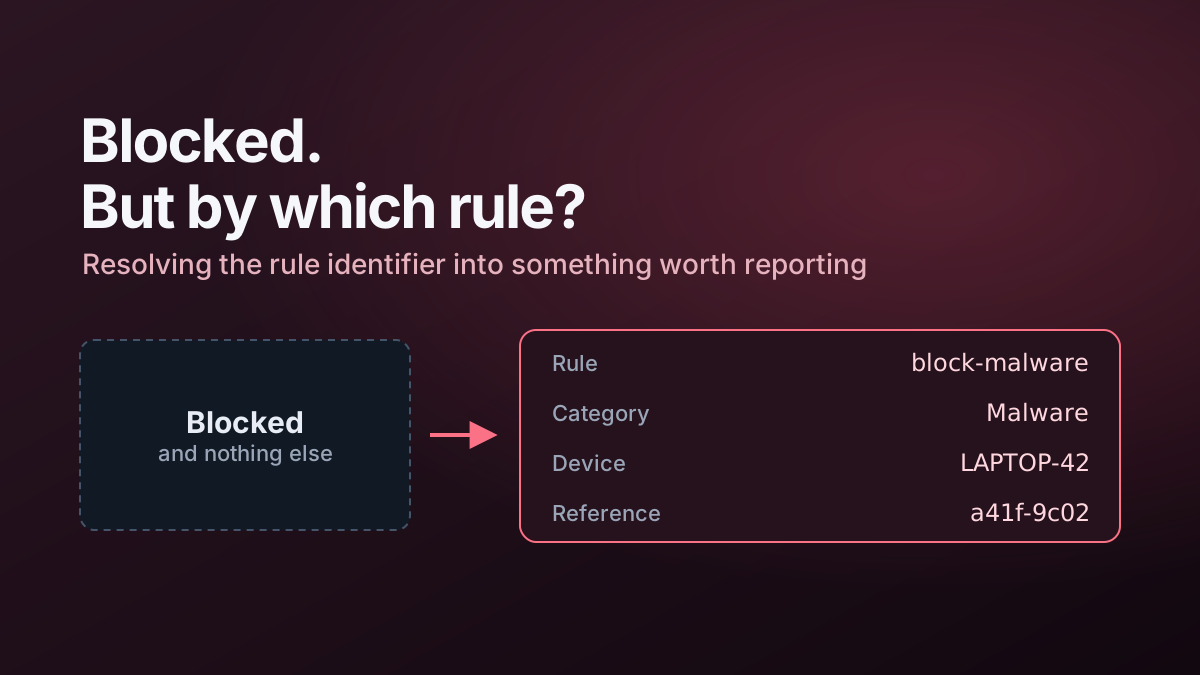
My block-page Worker looks for Gateway-specific query parameters such as:
cf_rule_id
cf_site_uri
cf_request_category_names
cf_user_email
cf_filter
cf_device_id
cf_ray_id
If none of that context is present, the Worker returns a simple 403 instead of rendering the full diagnostic page.
Query parameters are not secret, so this provides no authentication. What it does provide is a useful request-shape guard that stops the public Worker URL behaving like a normal diagnostic endpoint with no Gateway event behind it.
Authentication/authorization, API-token protection and output escaping remain separate controls.