A small Worker-generated HTML page often contains inline style or script because there is no separate asset pipeline.
That does not mean the Content Security Policy needs to allow all inline code.
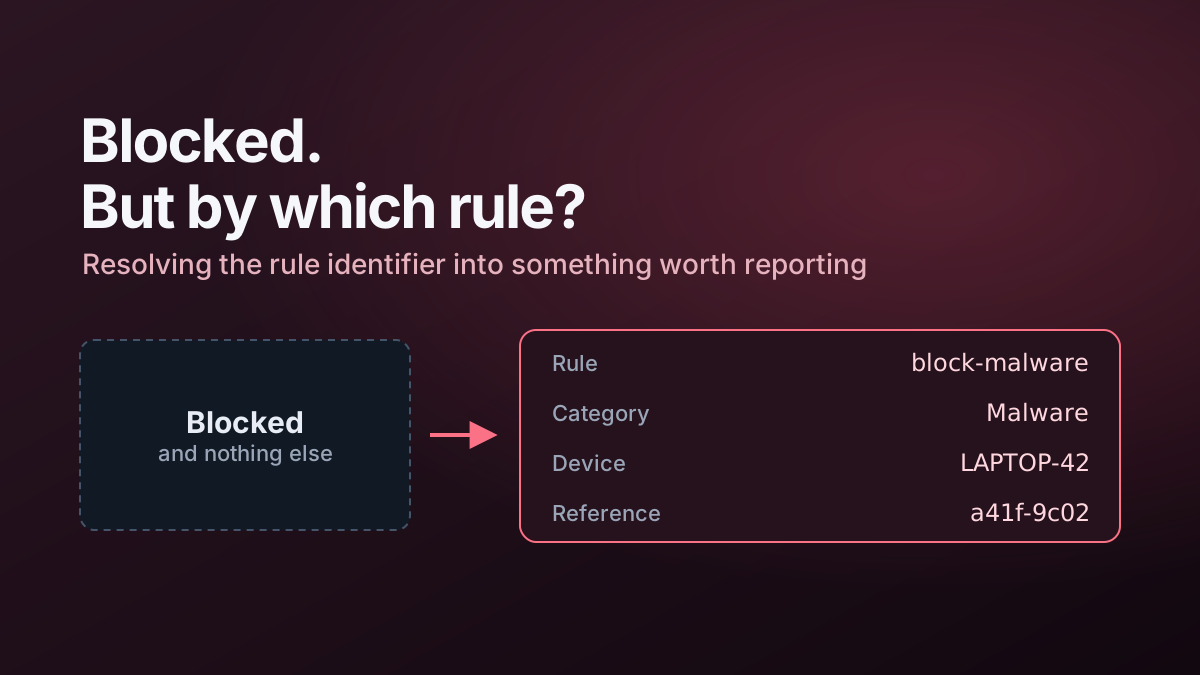
For my Gateway block page, the Worker creates a fresh nonce for each response:
const nonce = crypto.randomUUID().replace(/-/g, '');The same nonce is placed on the permitted <style> and <script> elements and in the CSP header:
style-src 'nonce-...';
script-src 'nonce-...';
Everything else can remain tightly restricted with directives such as:
default-src 'none'
base-uri 'none'
form-action 'none'
frame-ancestors 'none'
This is a good fit for small edge-rendered security pages because the nonce can be generated cheaply at request time and never needs to be persisted.