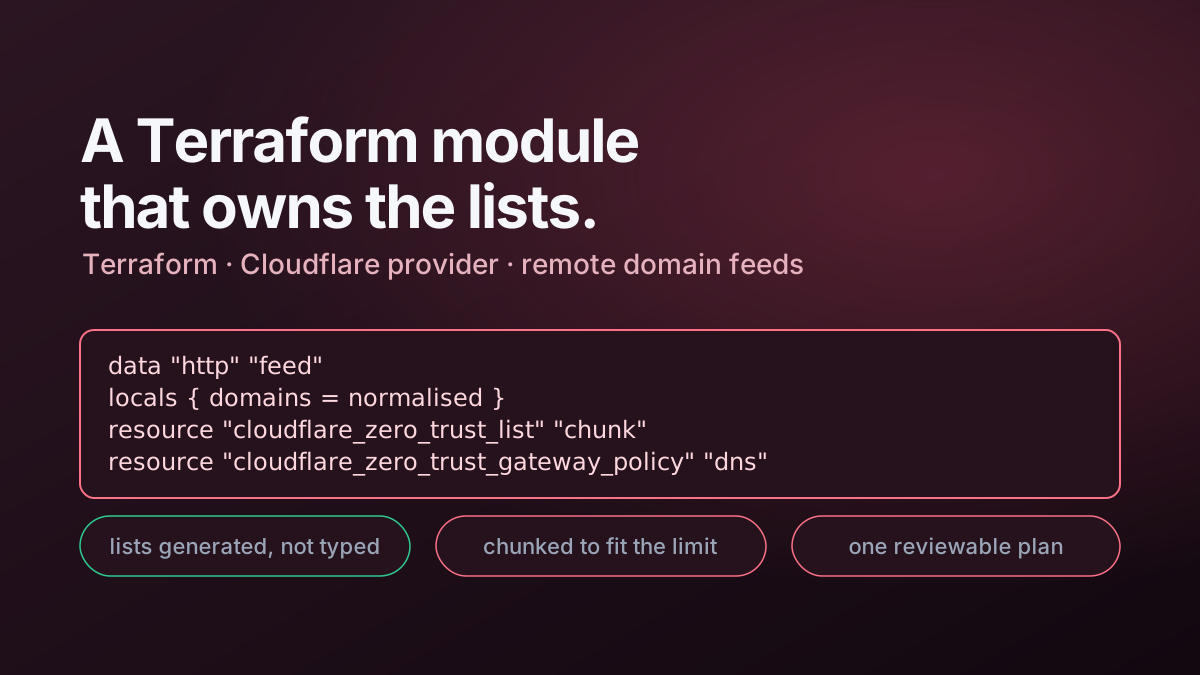
Terraform’s HTTP data source is a useful bridge when policy depends on a remotely published list.
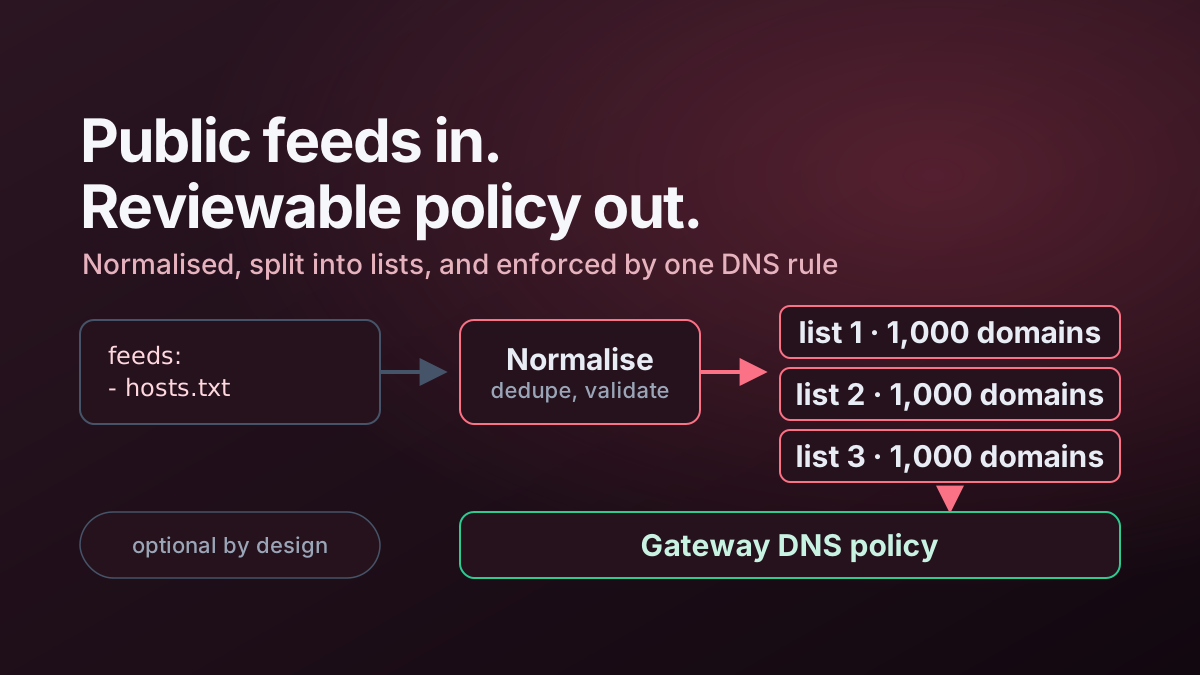
For my Cloudflare Gateway ad-blocking project, the flow is:
HTTP feed
  ↓
status validation
  ↓
line parsing
  ↓
normalization
  ↓
de-duplication
  ↓
Cloudflare domain lists
The important bit is the middle.
I do not want a remote response to become policy data simply because the request returned something. The configuration checks the response status and then converts supported feed formats into one canonical domain representation.
That keeps format-specific handling away from the eventual Gateway policy and makes the enforcement resources easier to reason about.
It also makes the external feed an explicit infrastructure dependency, which means source changes and unexpected deltas belong in normal review.
Related: DNS-Level Ad Blocking with Cloudflare Gateway and Terraform.