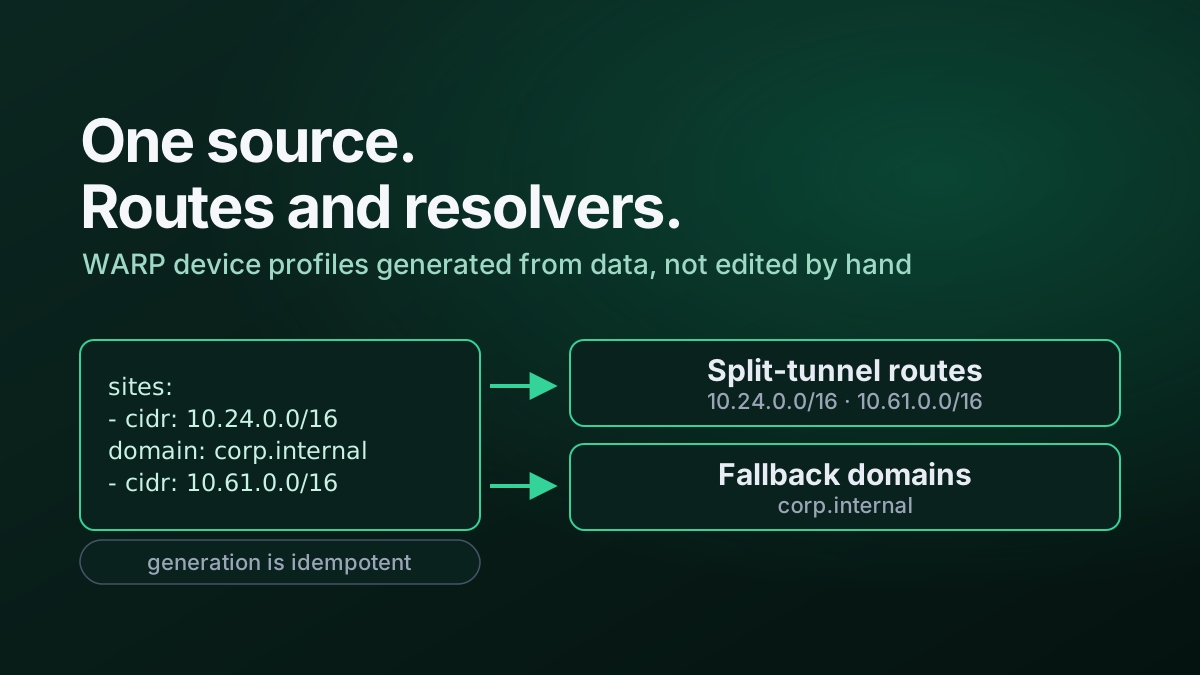
Private-network configuration drifts easily when the network is defined in Terraform but WARP routing is maintained manually somewhere else.
In my multi-cloud lab, a dedicated Terraform module calculates the routing subnets needed by the environment and exposes them as outputs.
The useful pattern is:
Cloud network definitions
        ↓
Terraform subnet values
        ↓
Routing calculation
        ↓
WARP / Zero Trust configuration
That does not mean every client policy must be generated automatically. It means I prefer infrastructure data to be the input when the same values are already authoritative elsewhere.
The alternative is duplication:
Terraform says subnet A exists
manual WARP list says subnet B exists
Once those two copies diverge, troubleshooting becomes much harder.
Related: Building a Multi-Cloud Zero Trust Lab with Cloudflare and Terraform.