Article
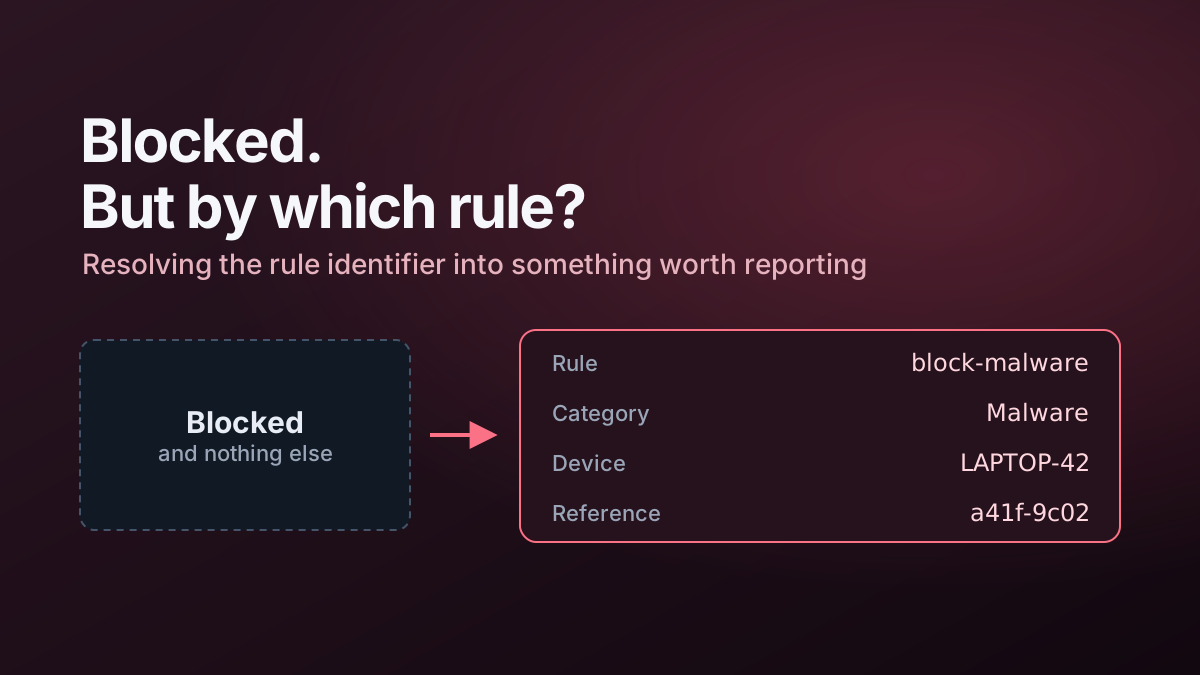
Building a Better Cloudflare Gateway Block Page
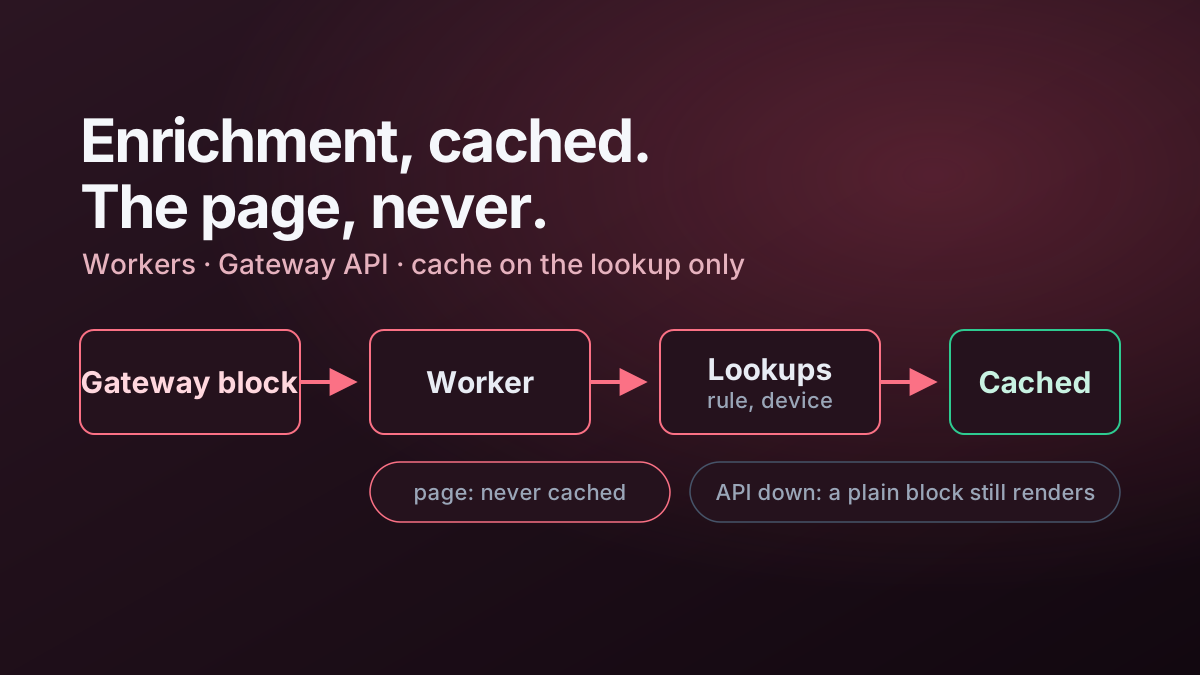
How I used a Cloudflare Worker to enrich Gateway blocks with policy, device, user, category and Cloudflare One Client context while keeping the page resilient and secure.
Topic
10 matching entries across Articles, TIL and Projects.
Long-form writing tagged WARP.
How I used a Cloudflare Worker to enrich Gateway blocks with policy, device, user, category and Cloudflare One Client context while keeping the page resilient and secure.
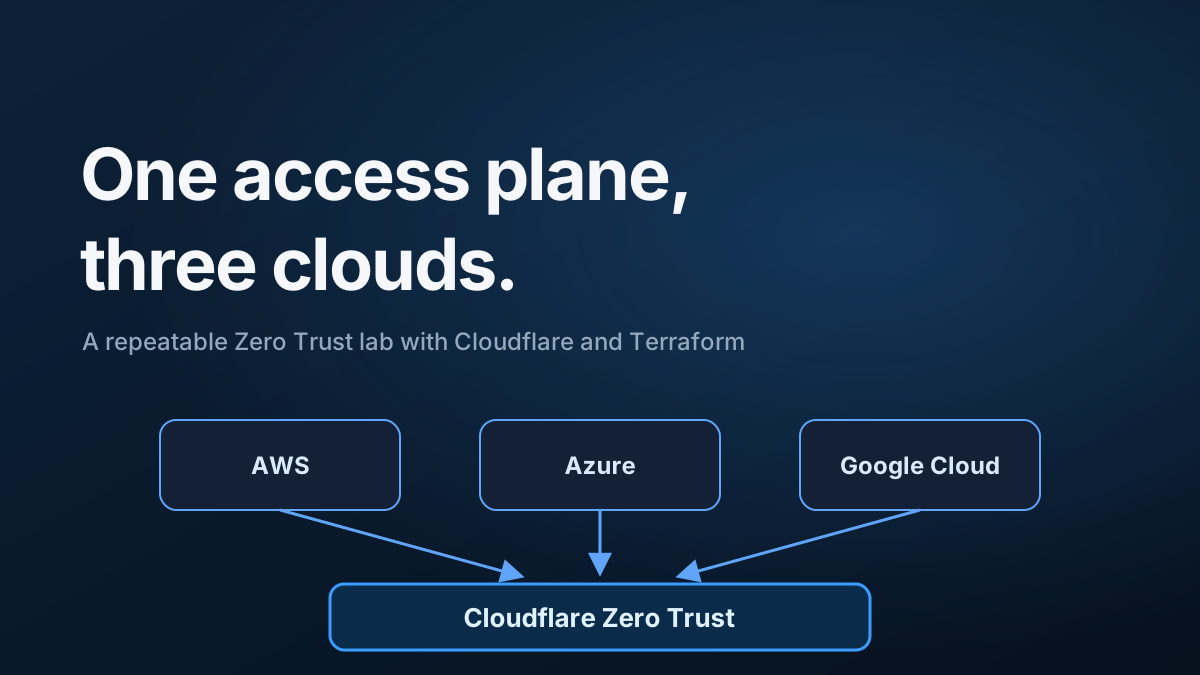
How I built a repeatable AWS, Azure and Google Cloud lab to explore Cloudflare Access, Gateway, WARP routing, device posture and external evaluation as one integrated Zero Trust system.
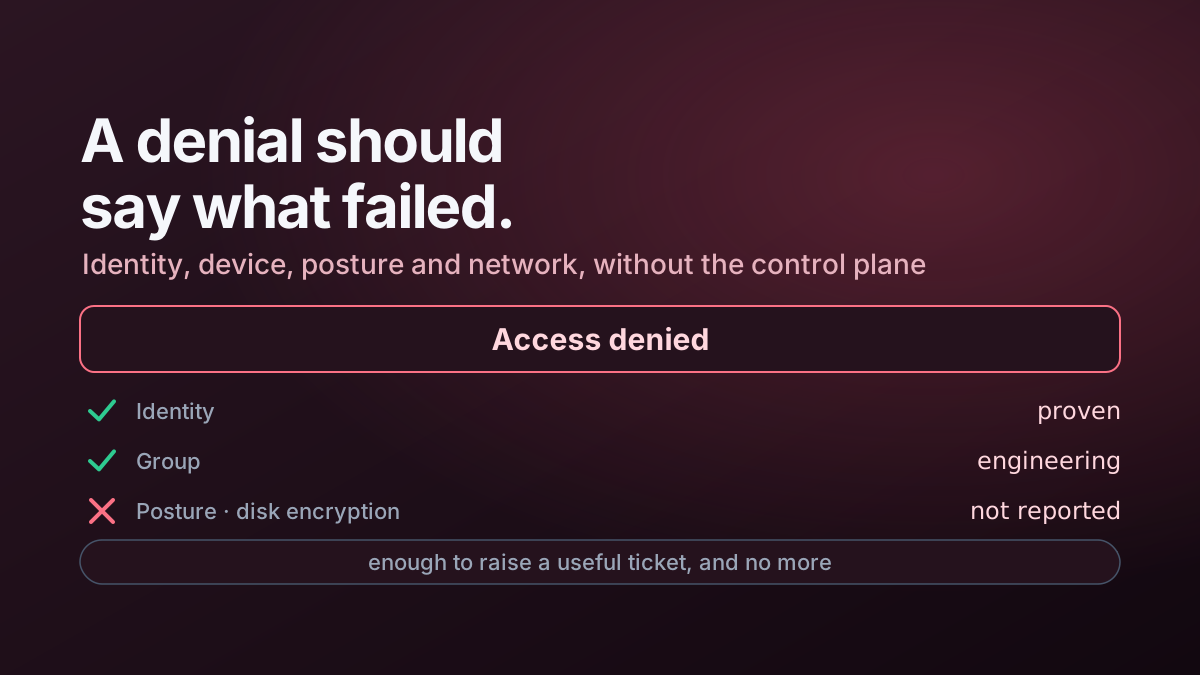
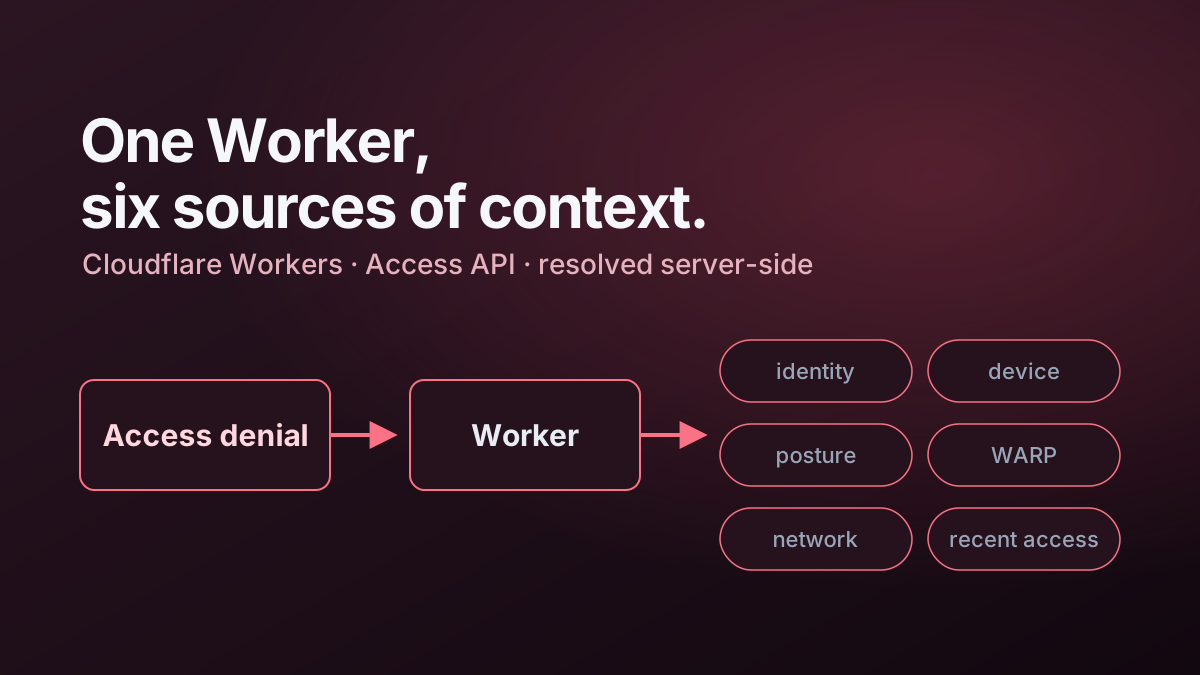
A custom Cloudflare Access denial page can turn a generic block into useful identity, device, posture and network diagnostics without exposing sensitive control-plane details.
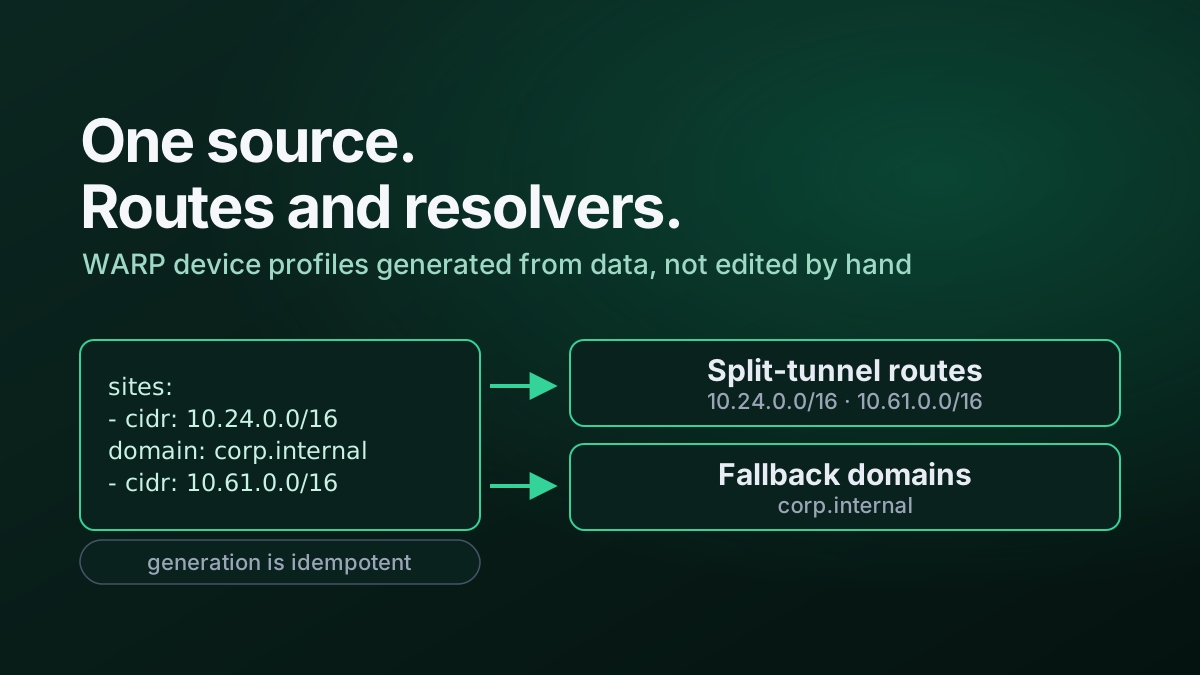
When private sites and DNS exceptions multiply, WARP device-profile configuration becomes data. Source control can become the input and PowerShell the generator.
Short notes and fixes tagged WARP.
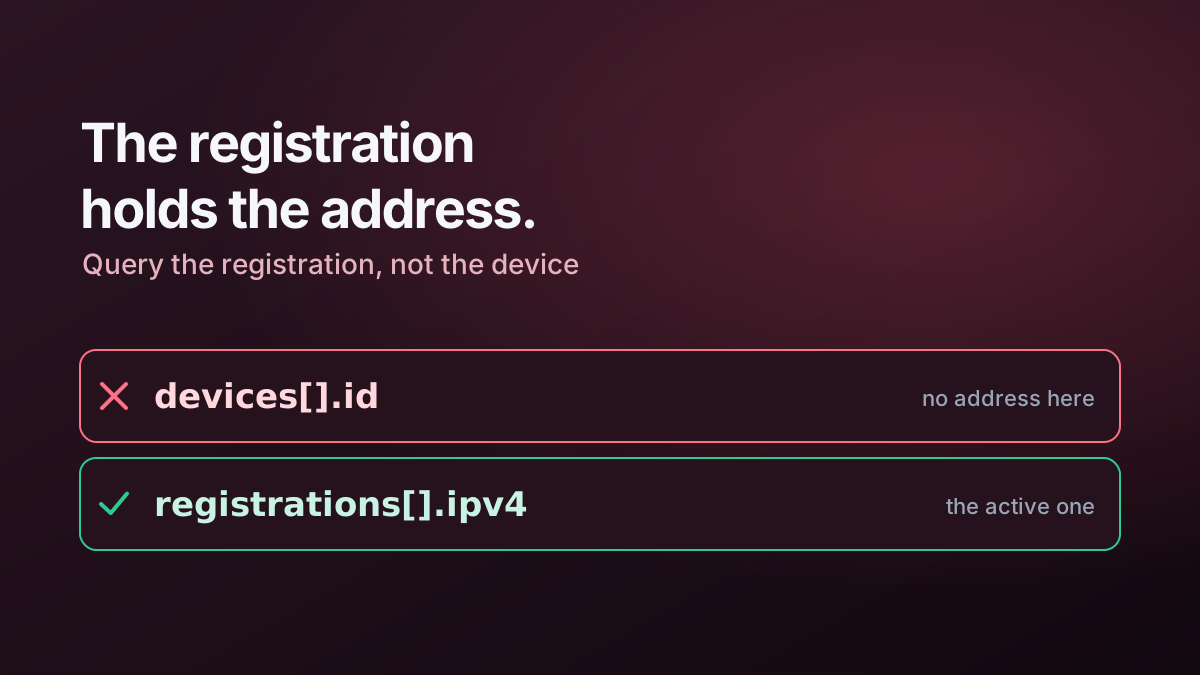
When a Zero Trust diagnostic page needs the virtual IPv4/IPv6 assigned to a device, the active device registration is the useful object to query.
When Terraform already knows the cloud subnets, those values can become inputs to WARP routing instead of being copied into a second manually maintained list.
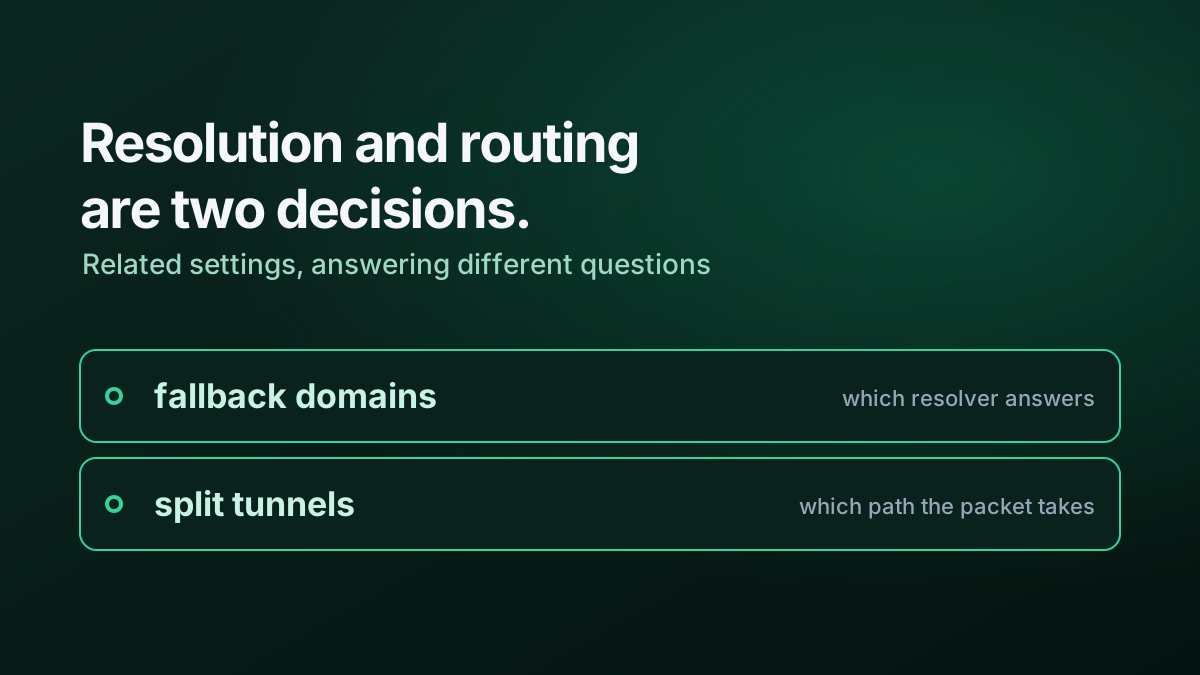
DNS resolution and packet routing are related, but a WARP configuration often needs you to reason about them separately.
Projects and implementation patterns tagged WARP.
A Cloudflare Worker that turns an Access denial into a support-friendly diagnostic page with identity, device, posture, WARP, network and recent-access context.
A Cloudflare Worker that enriches Gateway blocks with rule names, request category, user, device, Cloudflare One Client addresses and support correlation data.
A Terraform-managed Zero Trust engineering lab spanning AWS, Azure and Google Cloud with Cloudflare Access, Gateway, WARP routing, device posture and optional Worker integrations.