Suppose the requirement is:
Traffic to a particular SaaS application must leave through a controlled egress address.
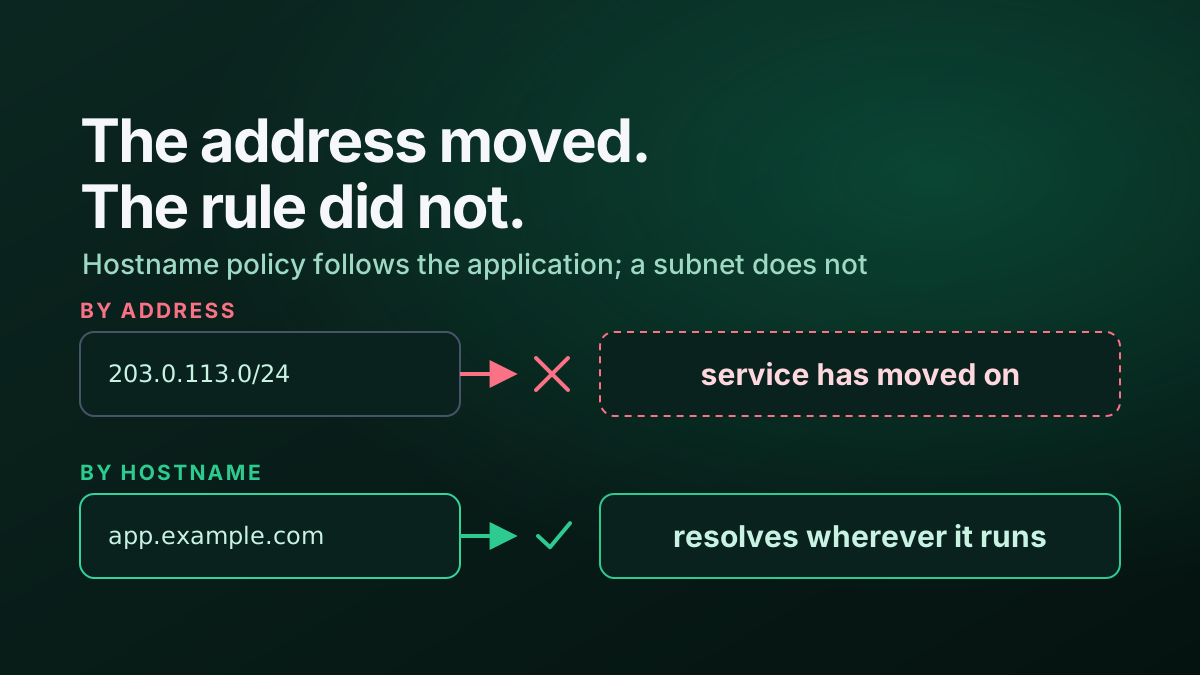
An IP-based rule can work, but cloud services and CDNs make the mapping increasingly fragile.
The business requirement is normally about:
application.examplenot:
whatever IP ranges happen to host it todayThat leads to a useful principle:
Where the platform supports it, express application policy using application identity rather than oversized infrastructure ranges.
Domain-aware policy can reduce:
- large provider subnet lists
- unrelated traffic being captured
- constant IP-range maintenance
- policies that are difficult to understand later
There are still important details to validate, particularly DNS behaviour, direct-IP connections and applications that cache addresses.
But as a policy primitive, a hostname can often represent the original intent much better than a changing collection of IP ranges.
For the longer version of this topic, see the full article on domain-aware egress steering.